

Alex Moshkov
@amoshkov
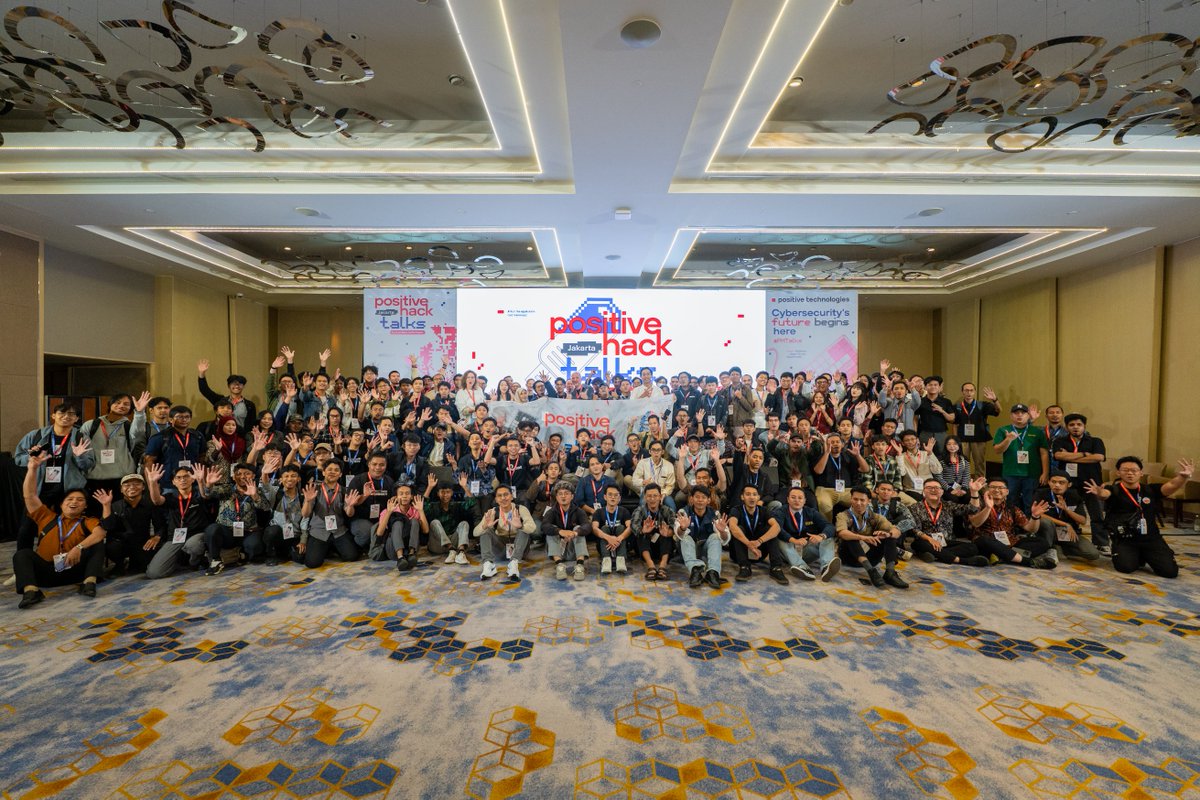
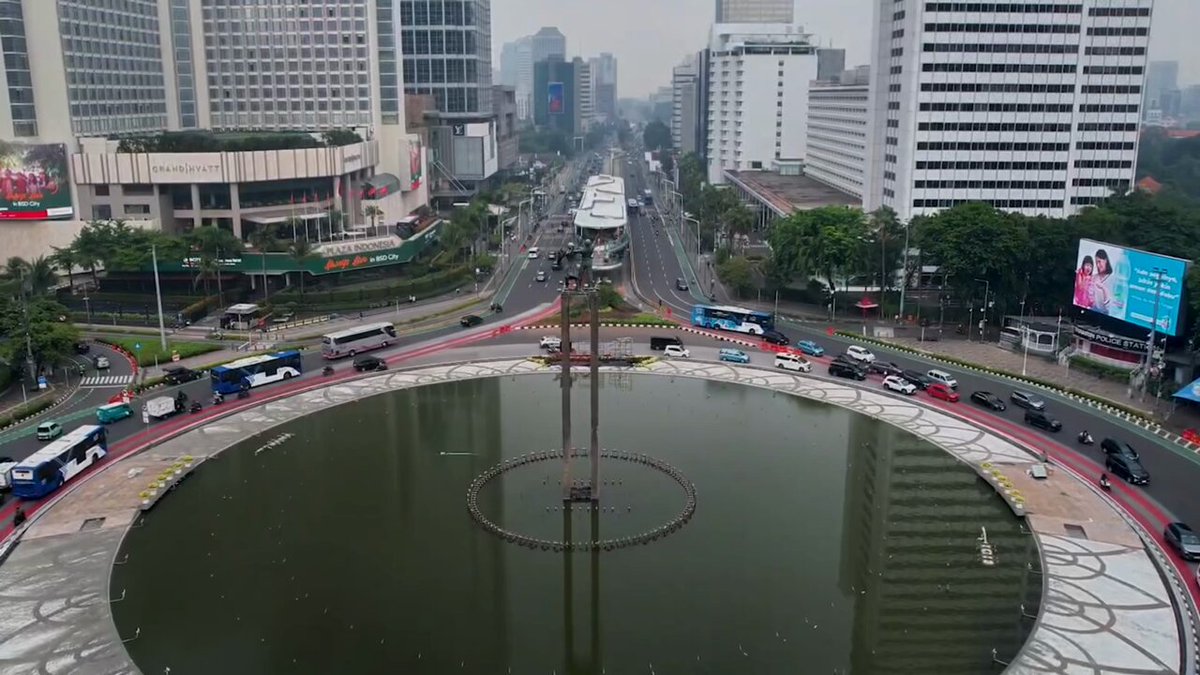
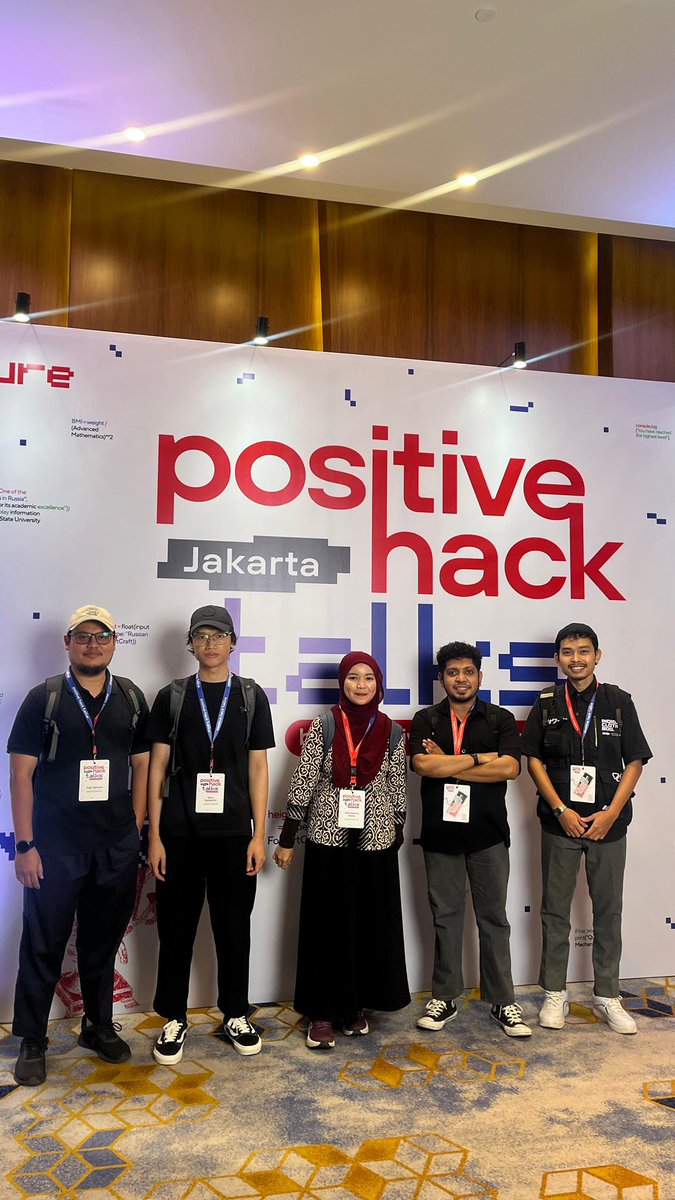
Another legendary shot from #PHTalks Jakarta — keeping this as a tradition for every next con! Unbelievable — 370+ attendees, a record for all past talks. And this photo shows just a part of them.
A free, community-driven cybersecurity conference where real hackers share what they've built, broken, and learned. No marketing, no nonsense. Brutally honest — just the way it should be.
A free, community-driven cybersecurity conference where real hackers share what they've built, broken, and learned. No marketing, no nonsense. Brutally honest — just the way it should be.
This stop took place on February 26, 2025.
Next stop: Goa, December 10, 2026 →Bug bounty, pentest, red team, OSINT. Real techniques, not theory.
Real cases — and how the vulns were actually found.
Grill the speakers. Answers you won't get from a blog.
Meet people who actually break things. No badge-scanning.
Another legendary shot from #PHTalks Jakarta — keeping this as a tradition for every next con! Unbelievable — 370+ attendees, a record for all past talks. And this photo shows just a part of them.

370+ #cybersecurity pros. 8 amazing talks by @cnwatcher @shipcod3 @pyn3rd @nalen98 @ElementalX2 @BukanYahya 1 epic #PHTalks Jakarta From car hacking to AI-powered detections — we brought it all Slides & Photos: https://t.co/4UZX2BQXI0 Share highlights and tag #PHTalks

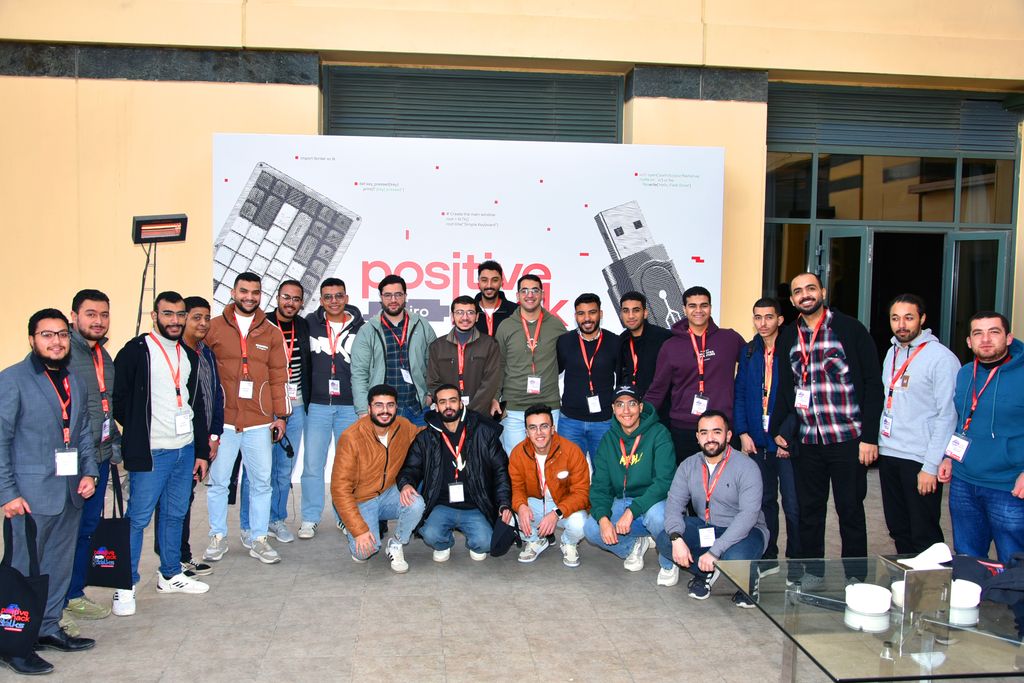
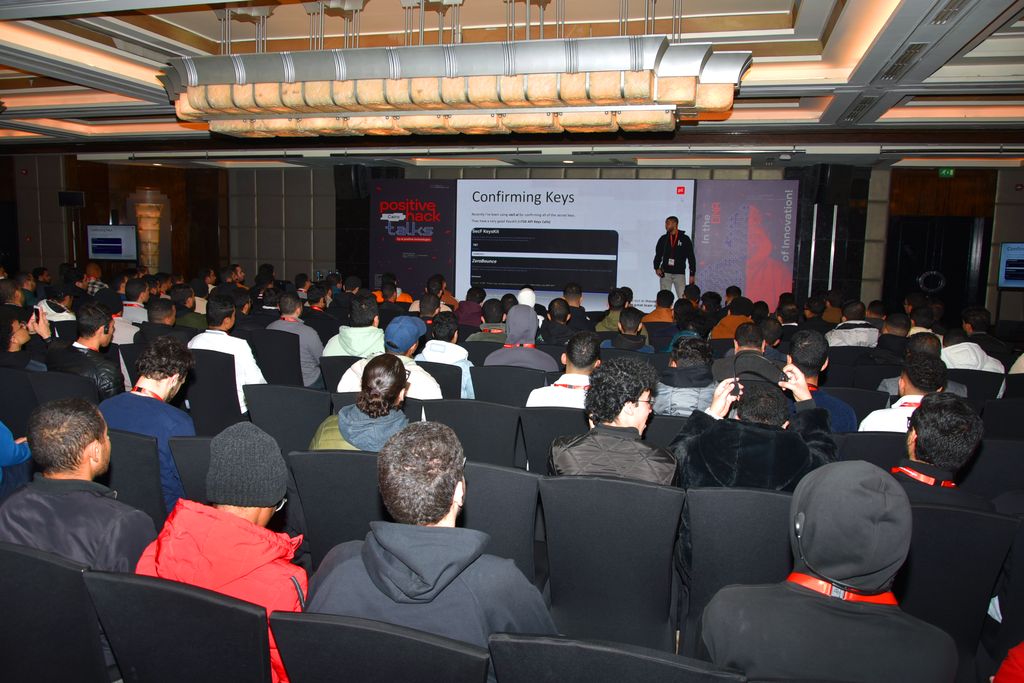
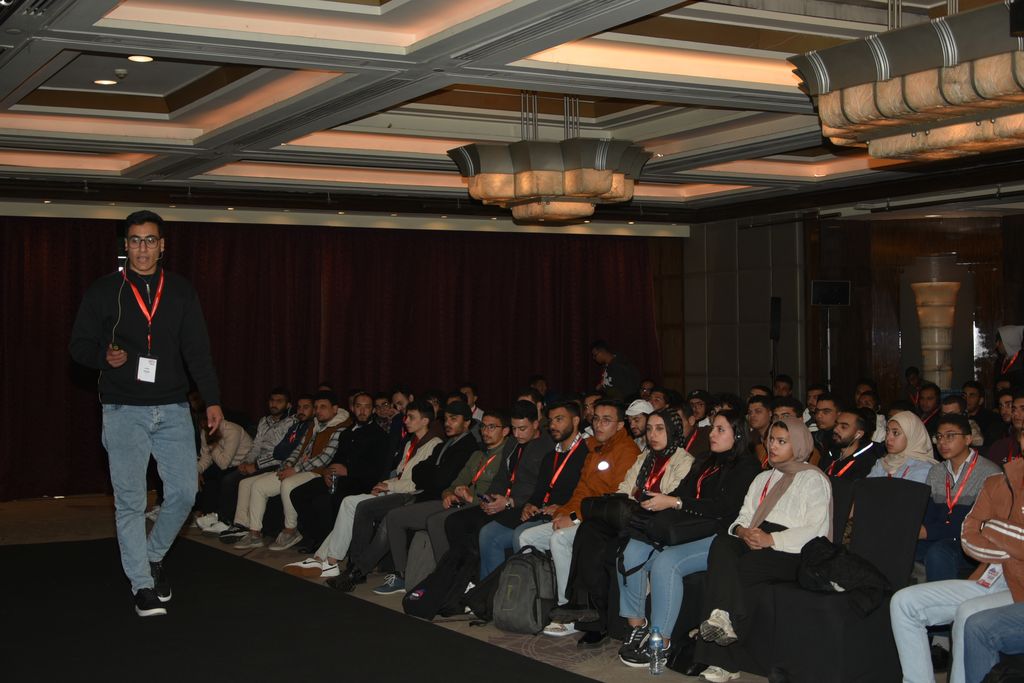
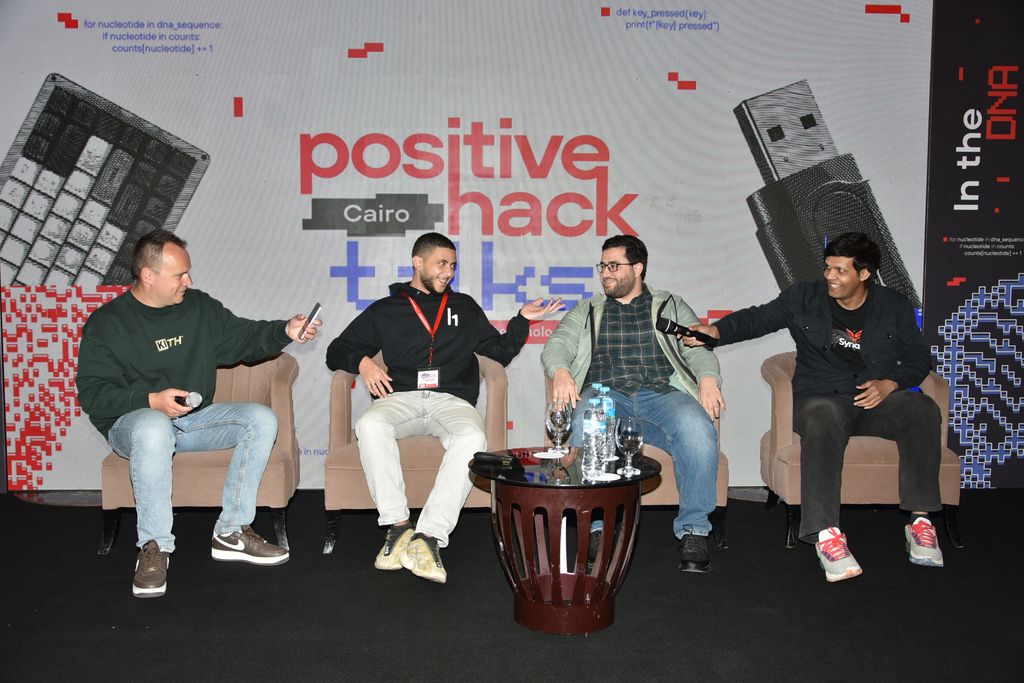
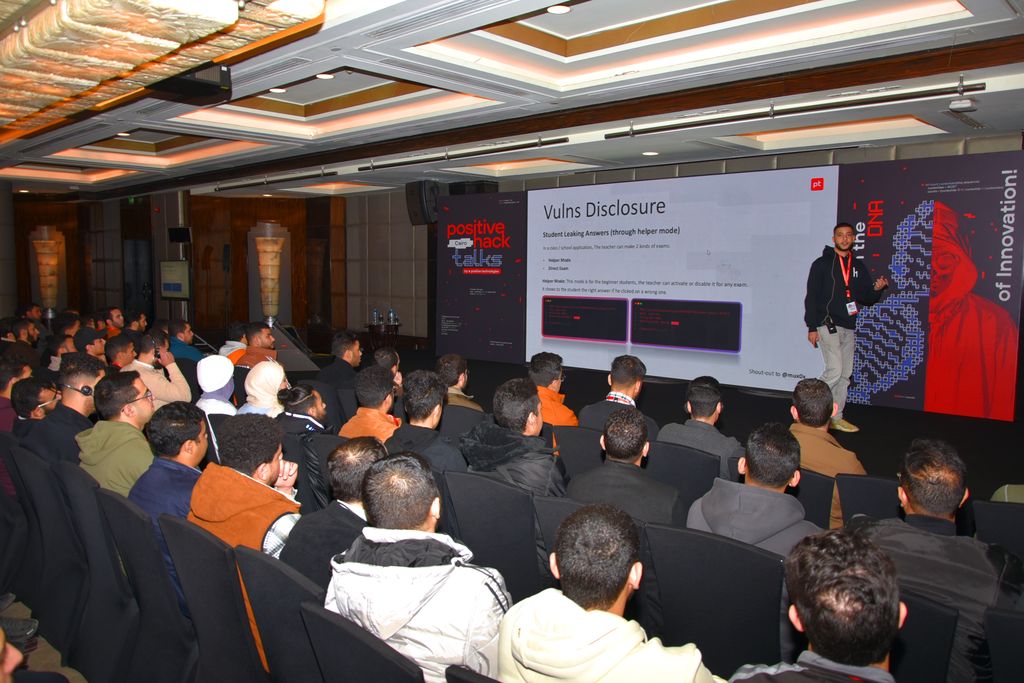
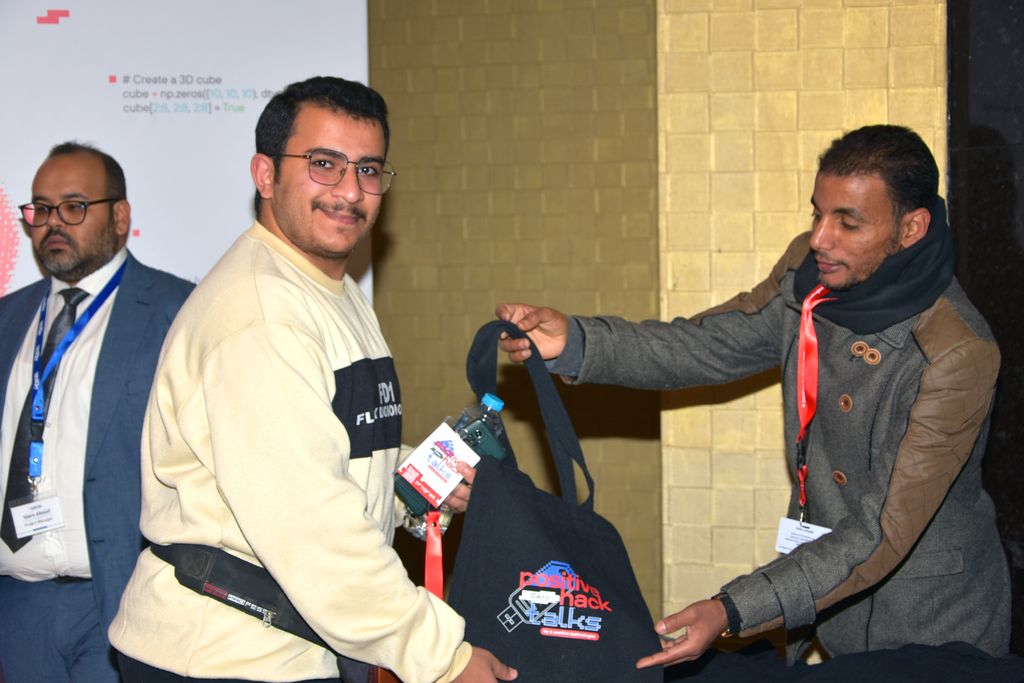
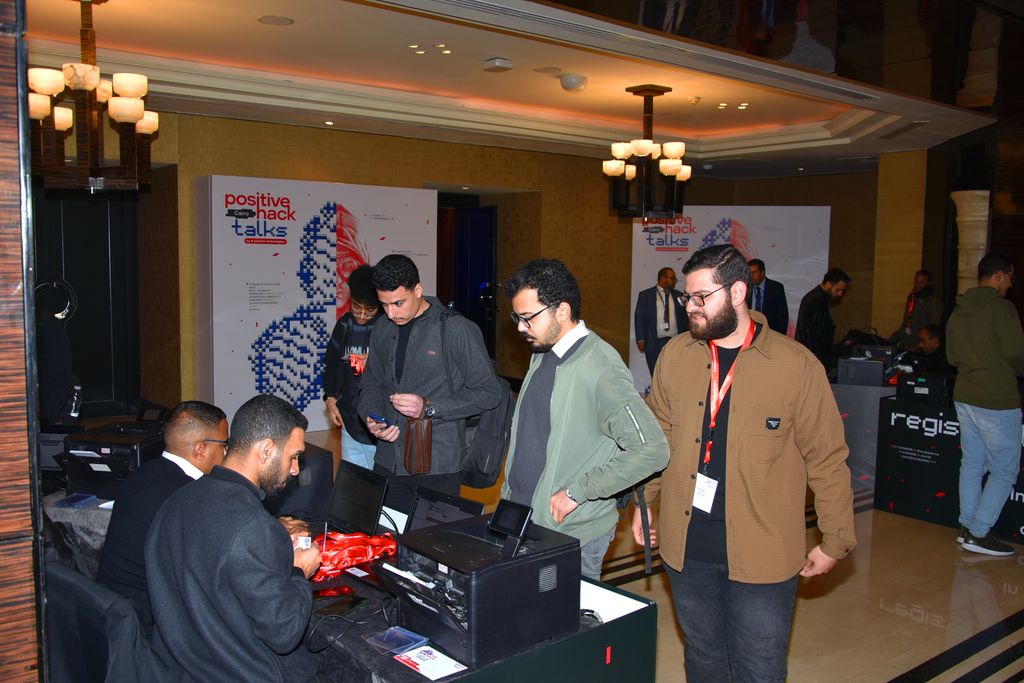
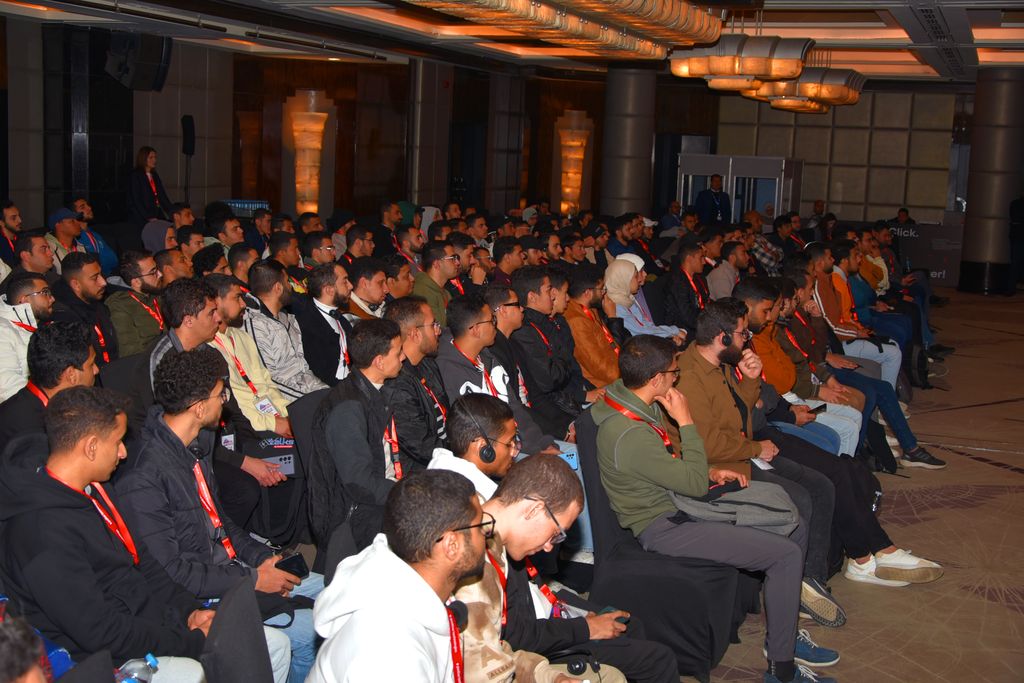
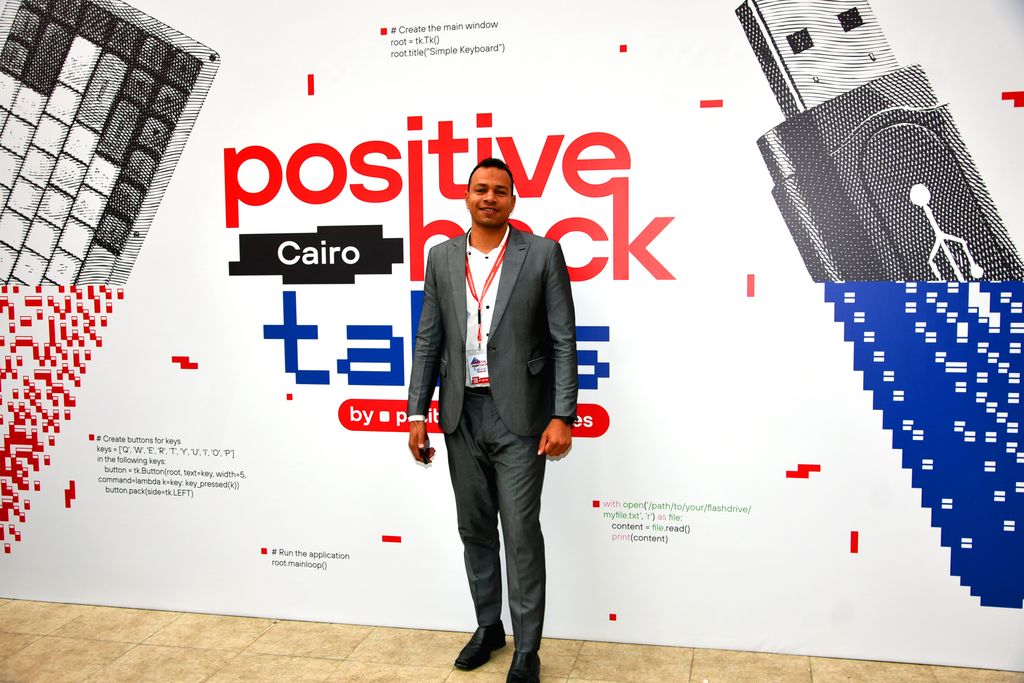
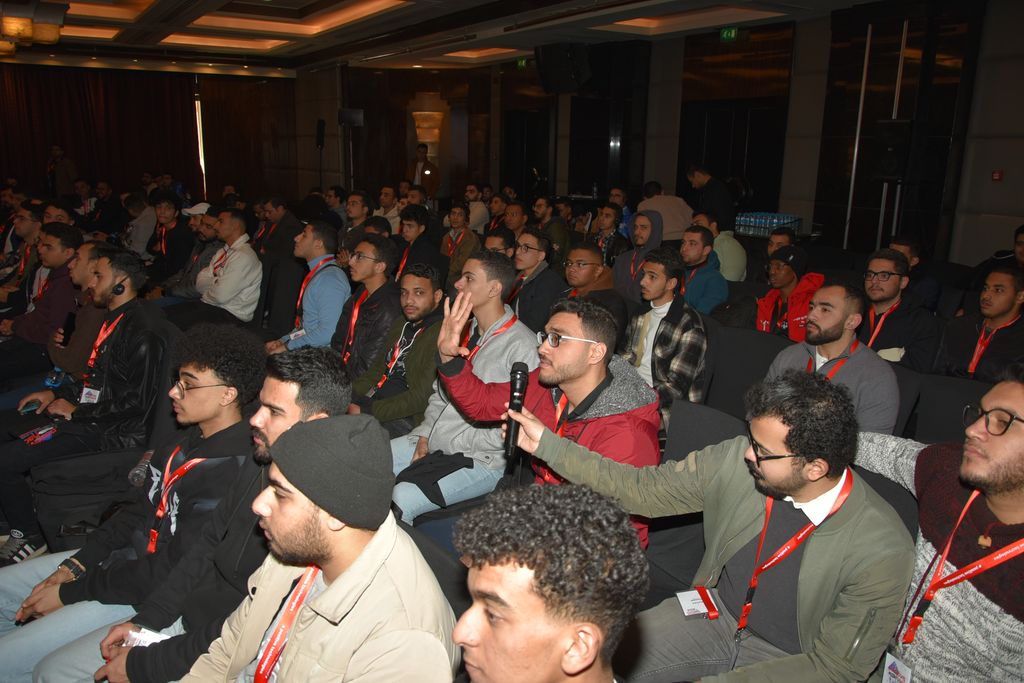
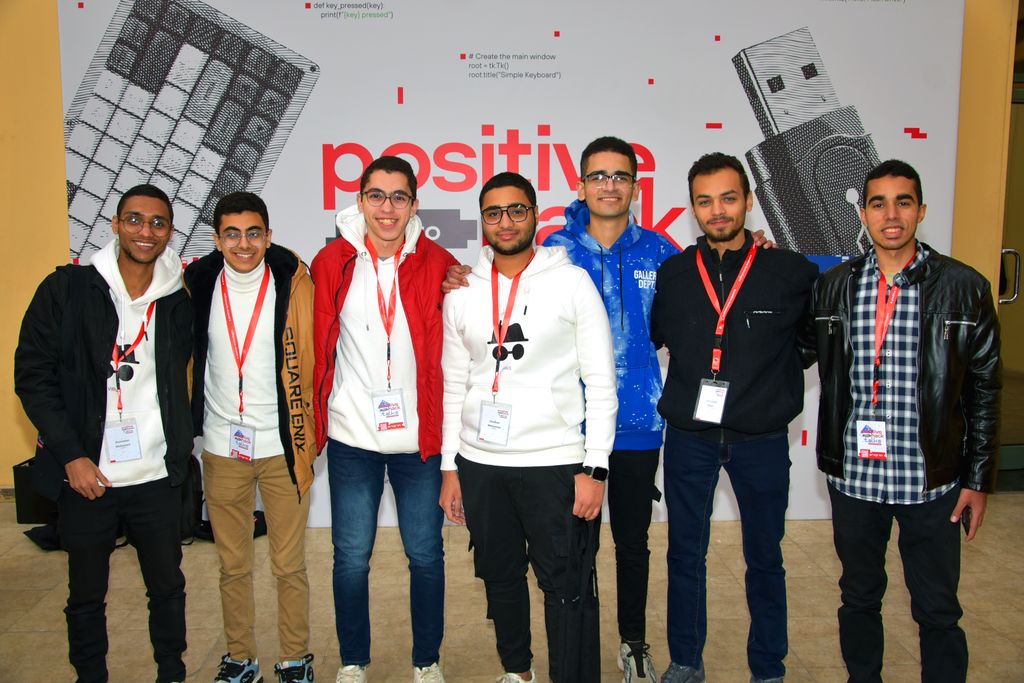
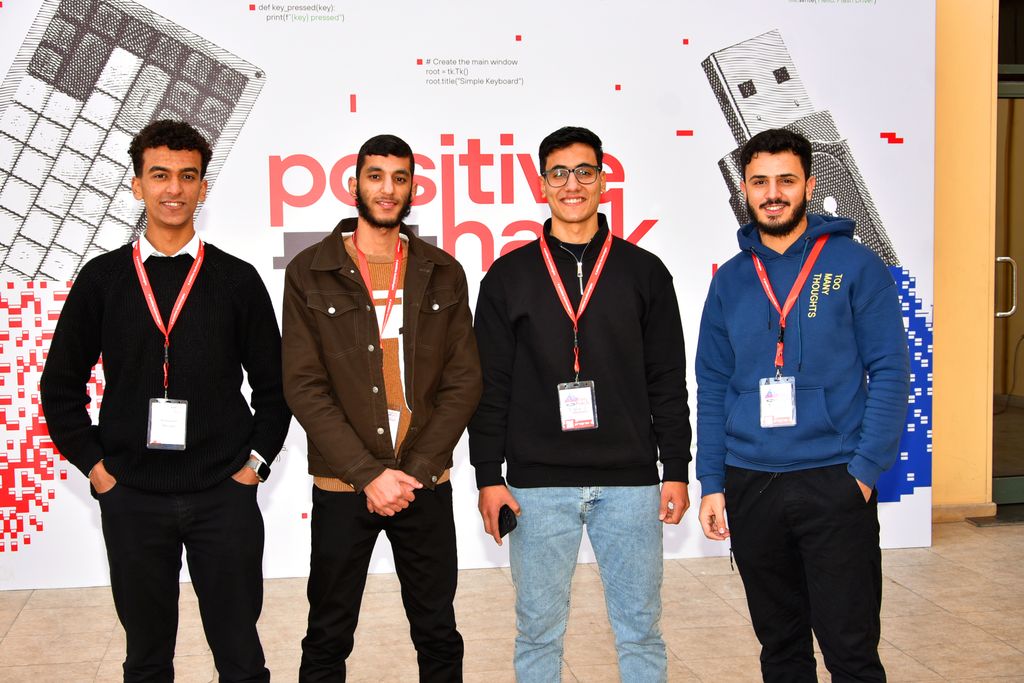
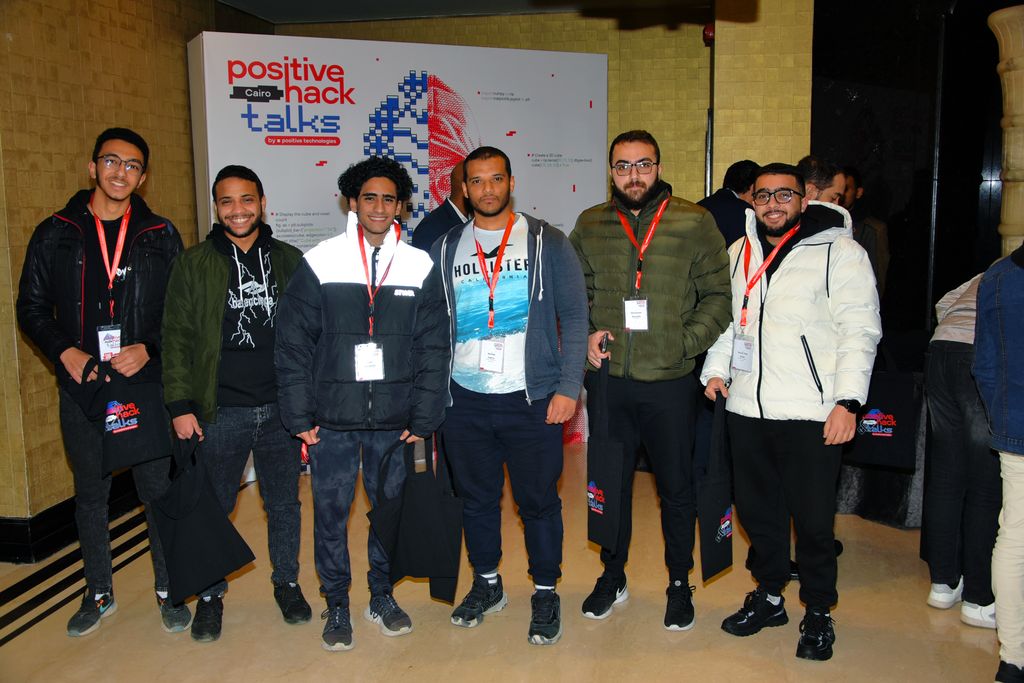
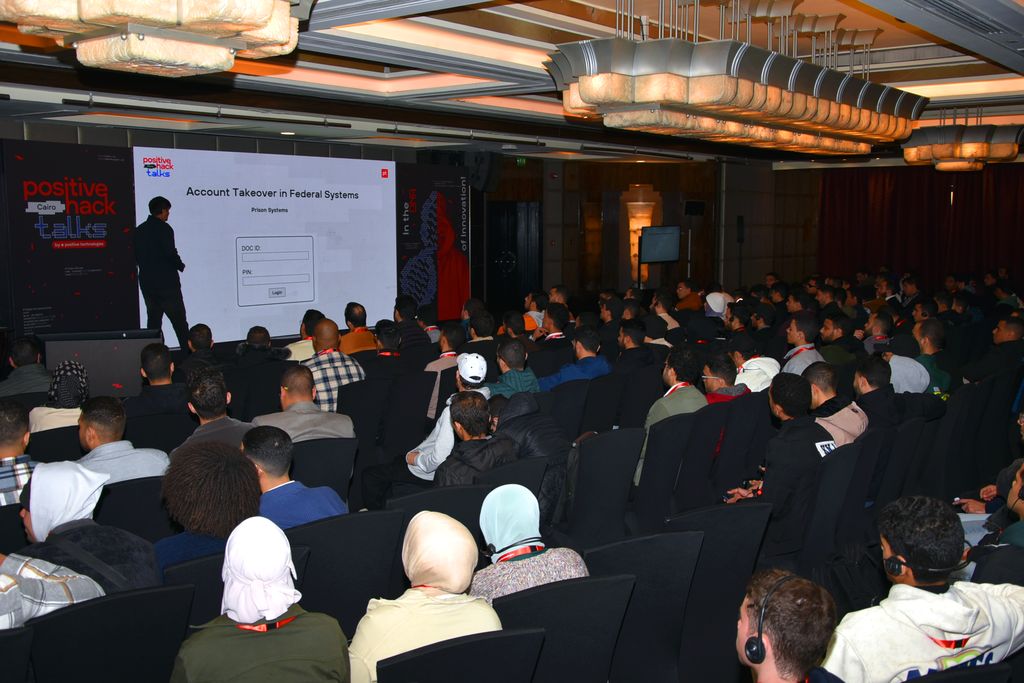
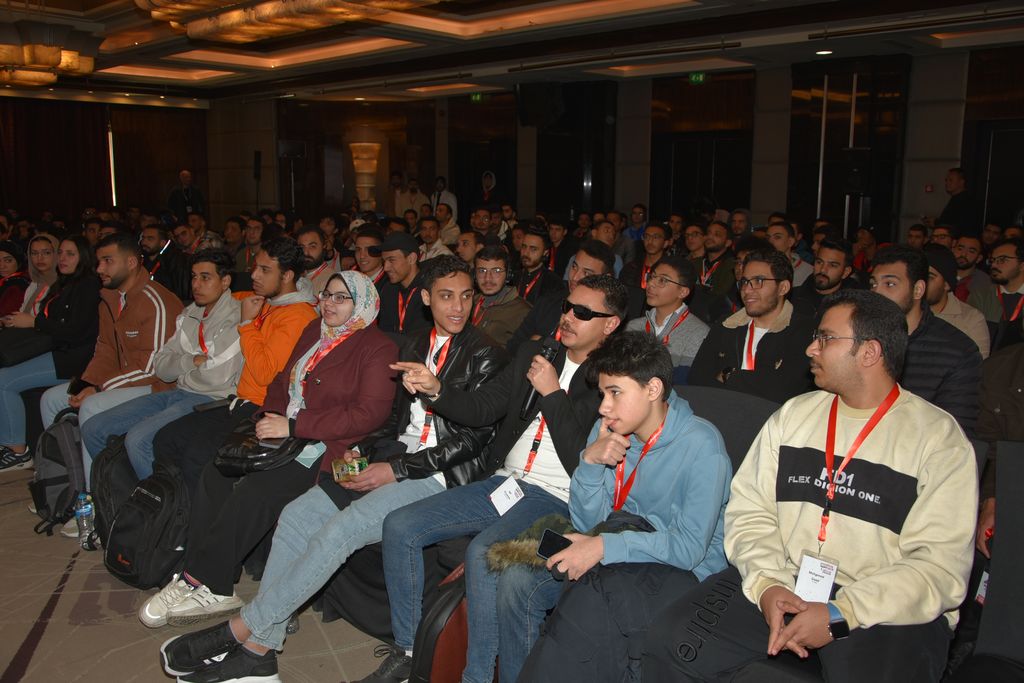
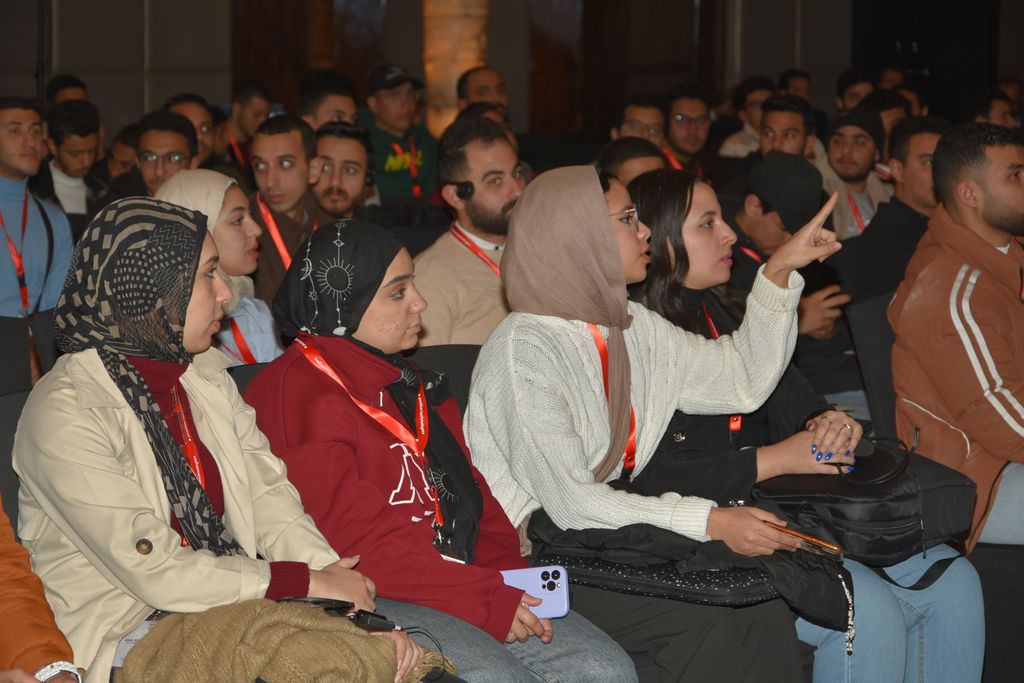
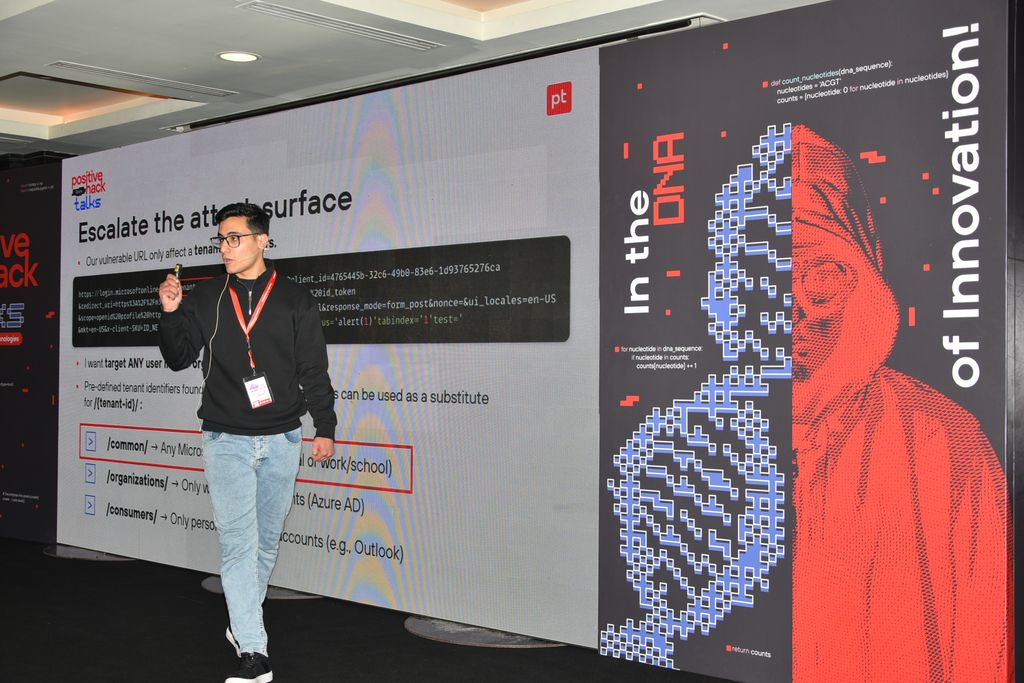
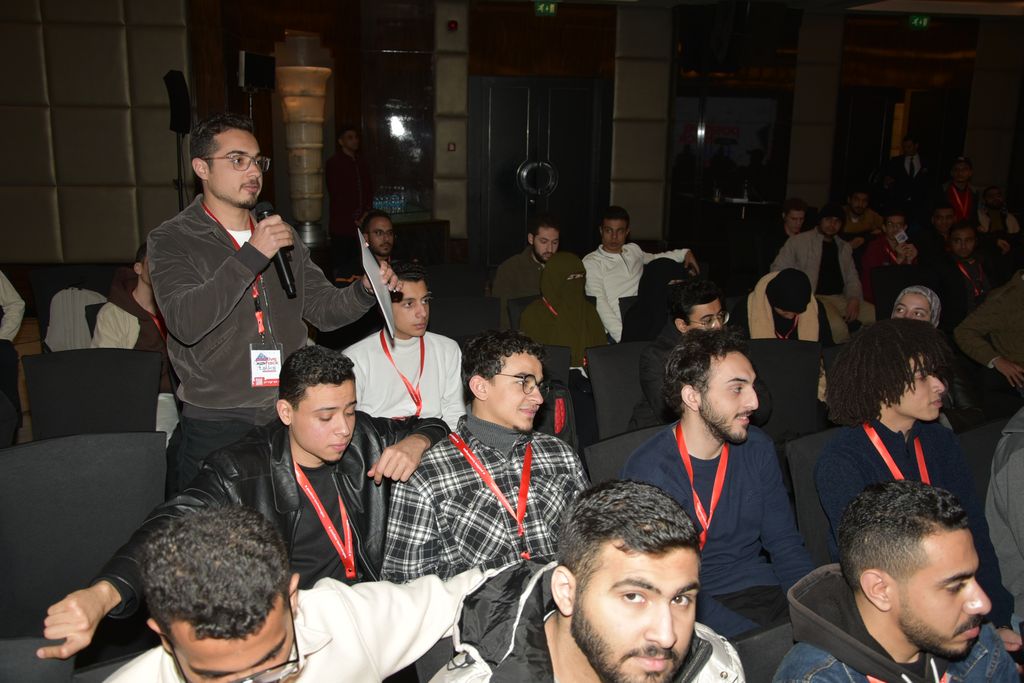
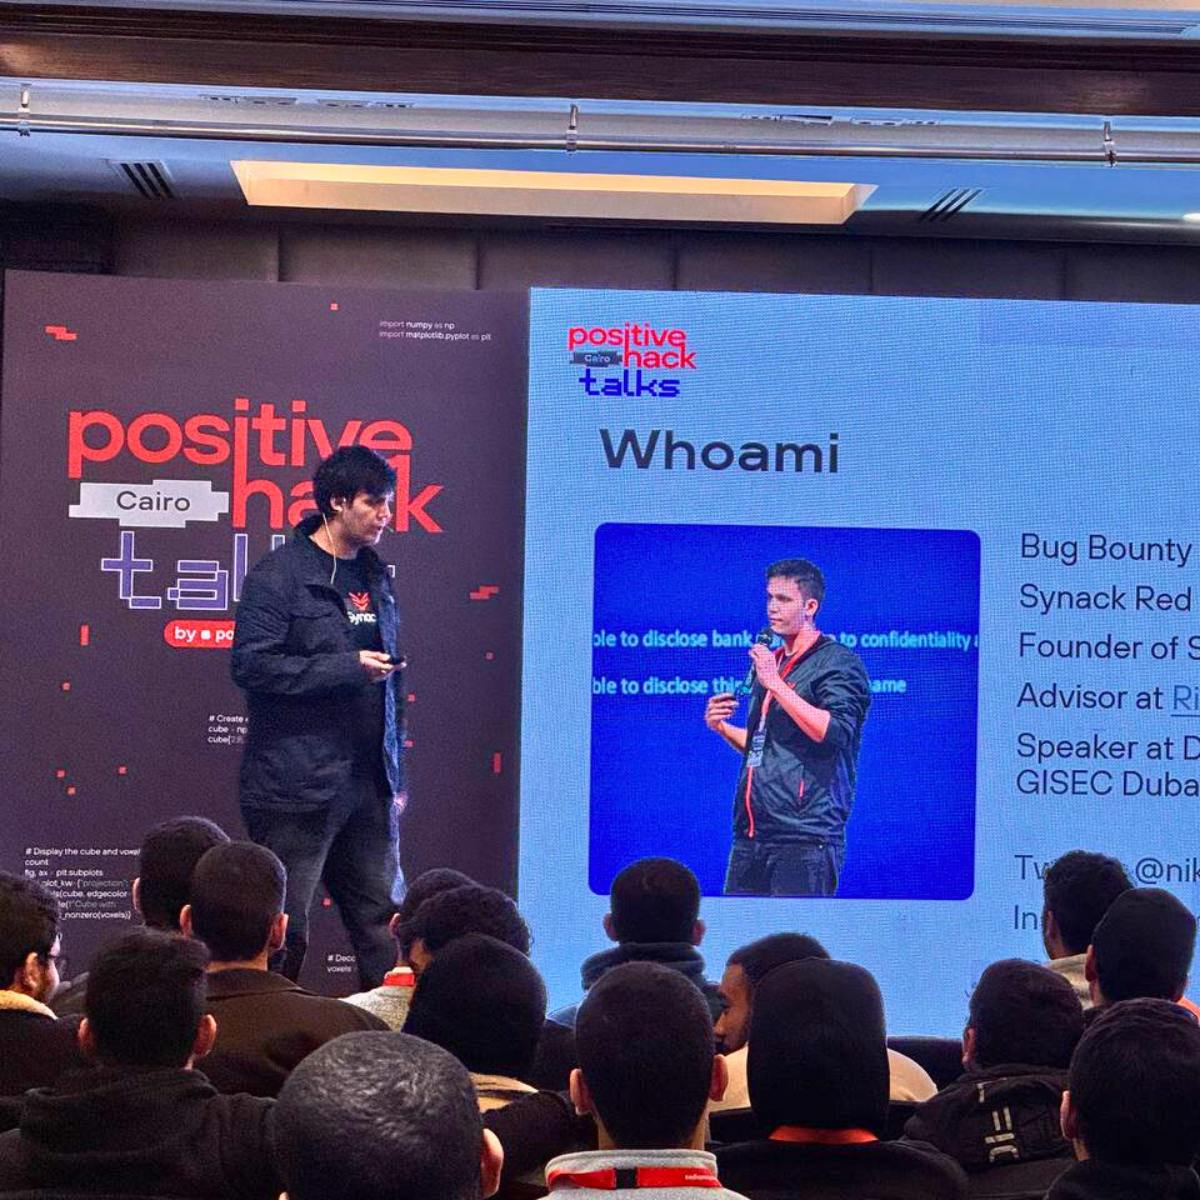
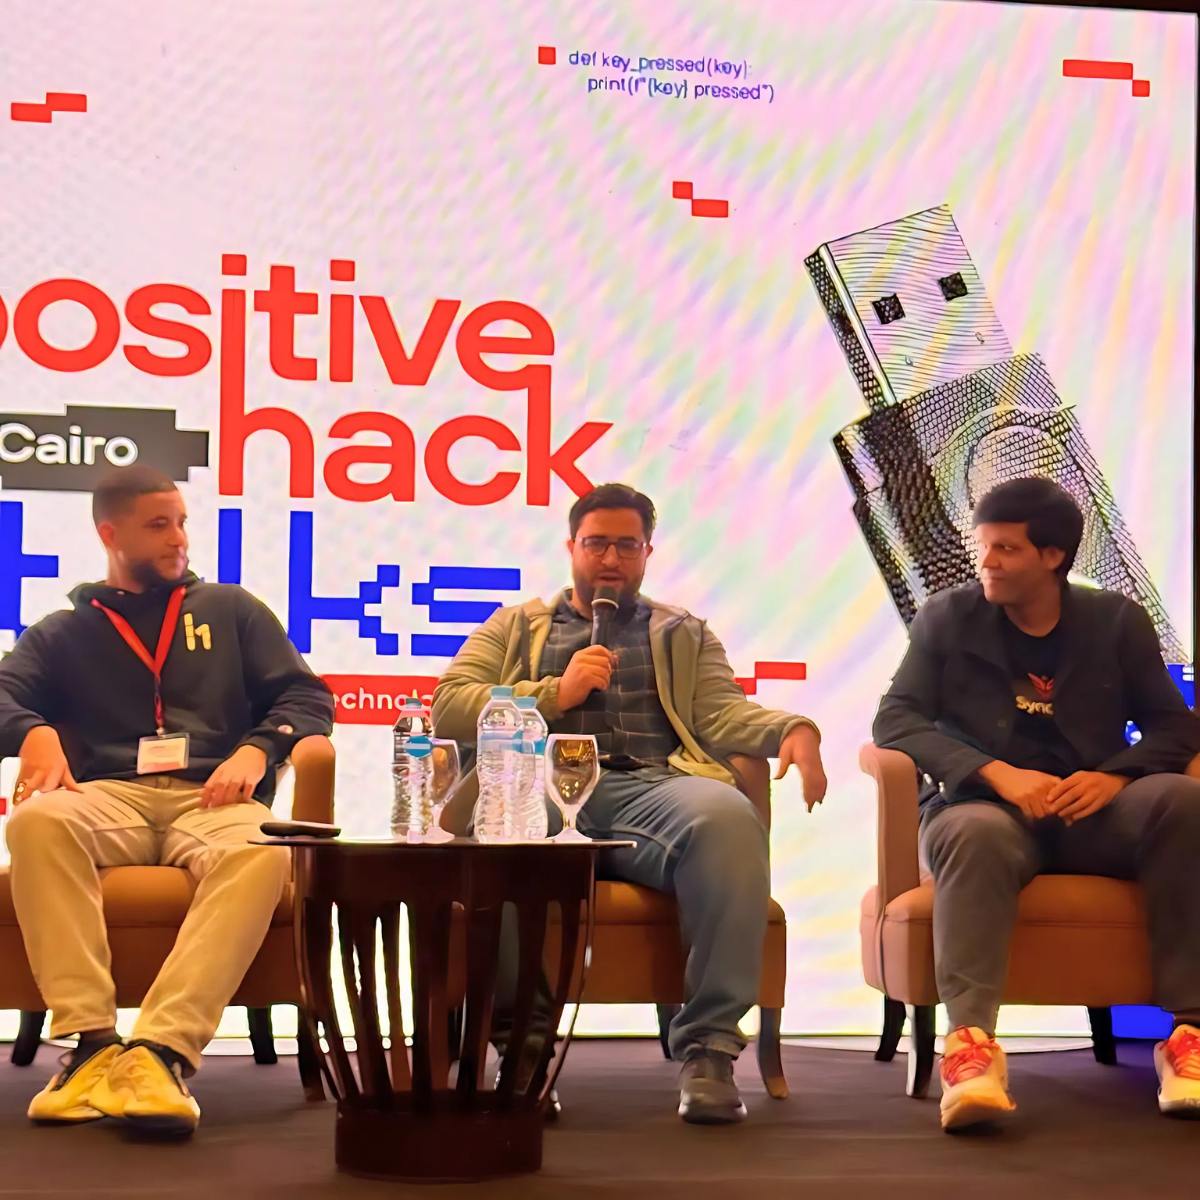
#PHTalks landed in Cairo, Egypt On February 26, the event brought together 200+ hackers for an intense exchange of ideas. An in-person meetup for cybersecurity specialists ready to absorb the latest knowledge on offensive and defensive security and bug hunting.
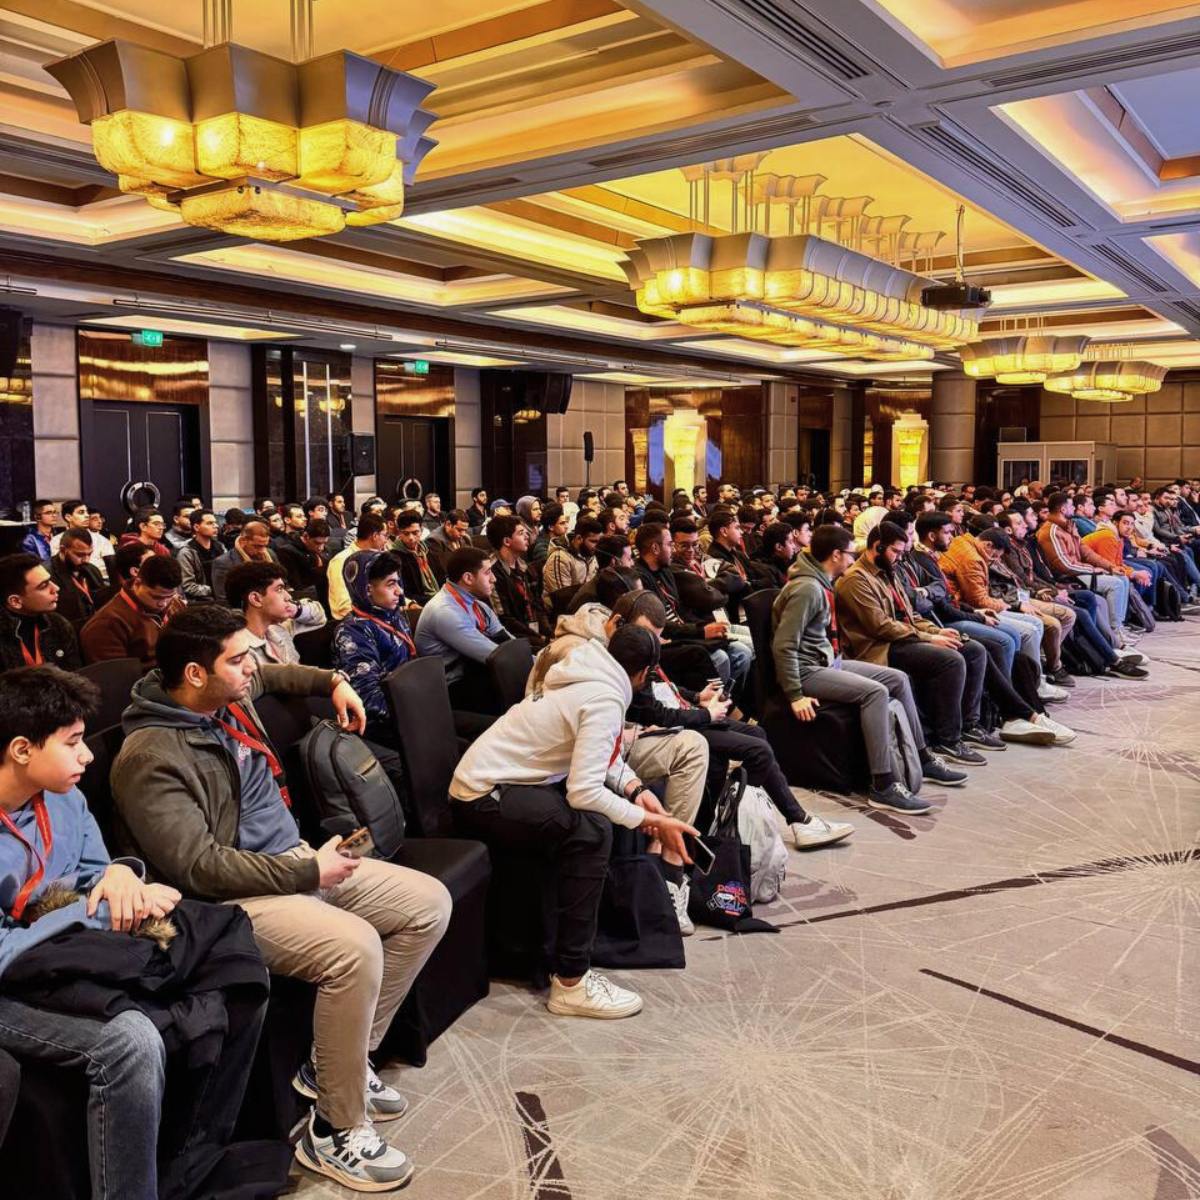
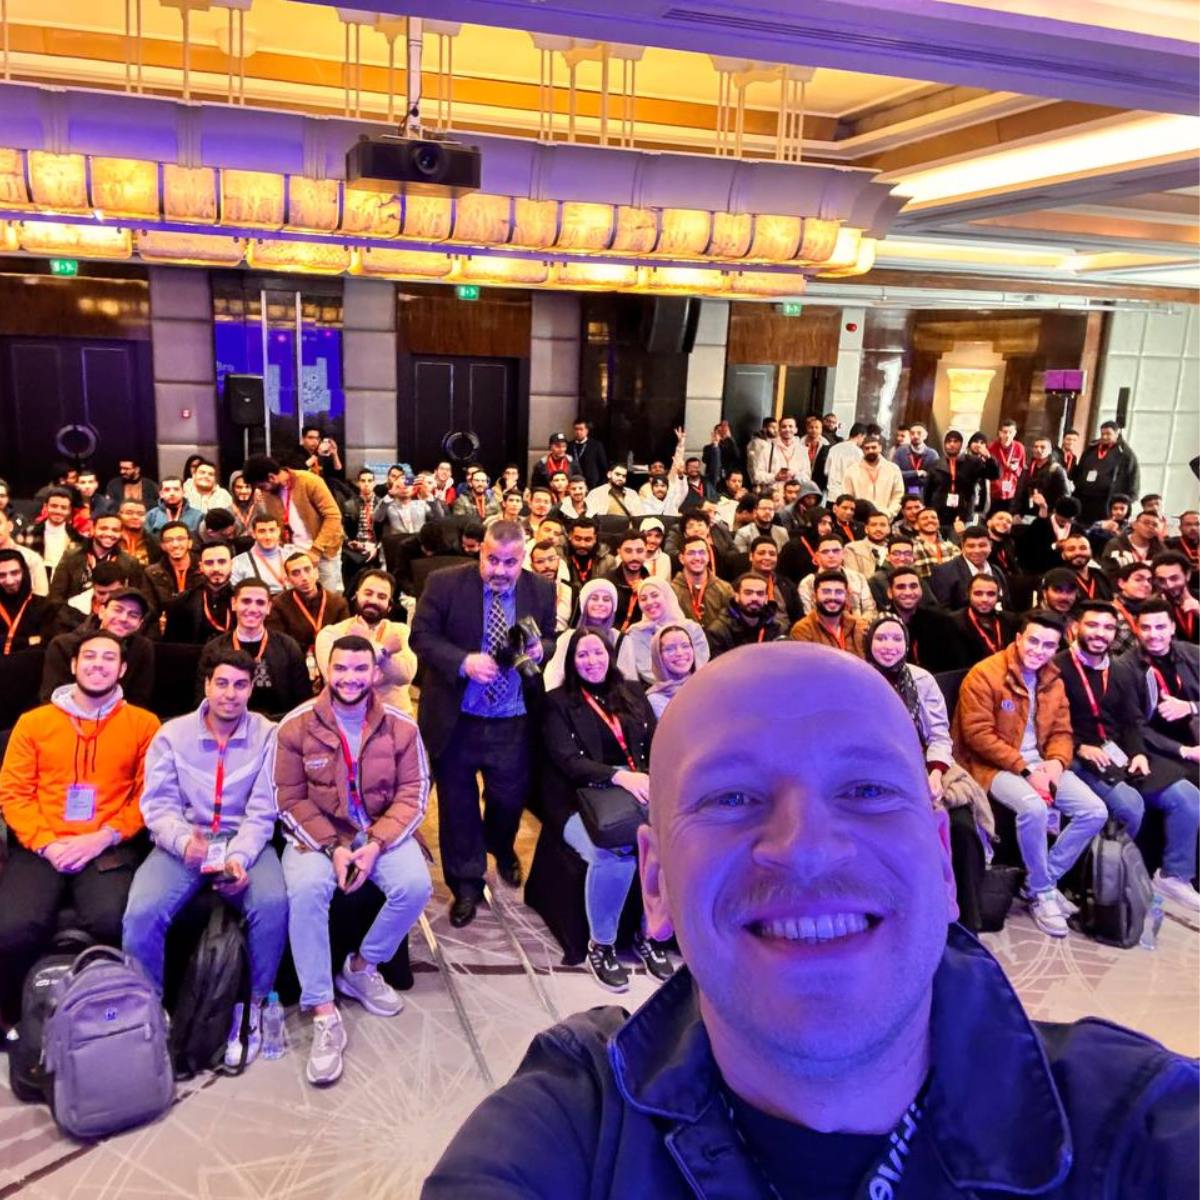
Thanks, Hanoi! Over 200 cybersecurity pros joined Positive Hack Talks for expert insights, hot topics, and great networking. From bug hunting to tackling top threats, it was a day to remember. Shoutout to our speakers! See you next time! #Cybersecurity #PHTalks
Idk guys — @nizarakbarm @Nalen98 @shipcod3 @BukanYahya @screetsec @ElementalX2 — not sure how it happened, but we've got no proper group photo together from #PHTalks Jakarta. So here's what I managed to collect
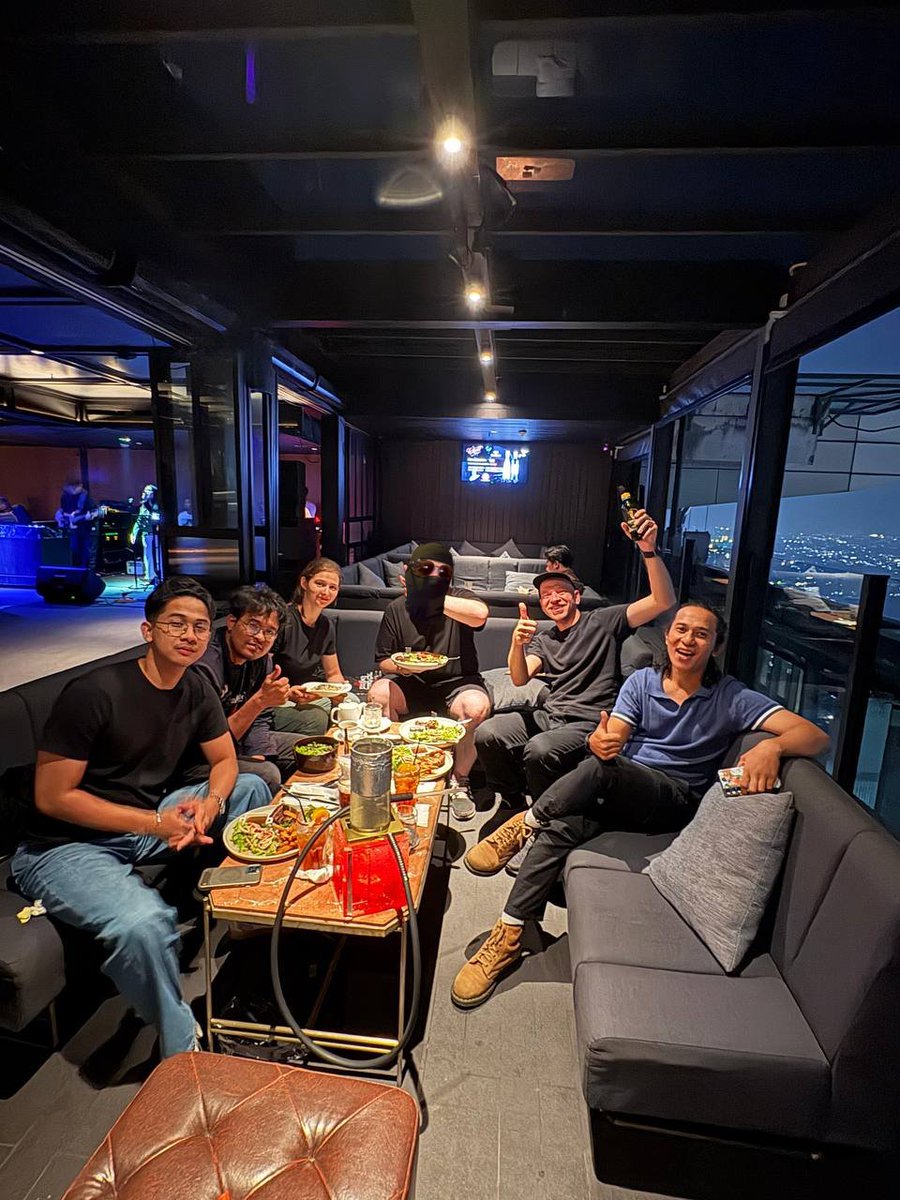
An incredible experience before the #PHTalks. Thank you all so much!!@SirBagoza @niksthehacker @naumovax @rosako @amoshkov @0xMalWan @Ellord0Xd @m359ah @SergeyTemnikov2
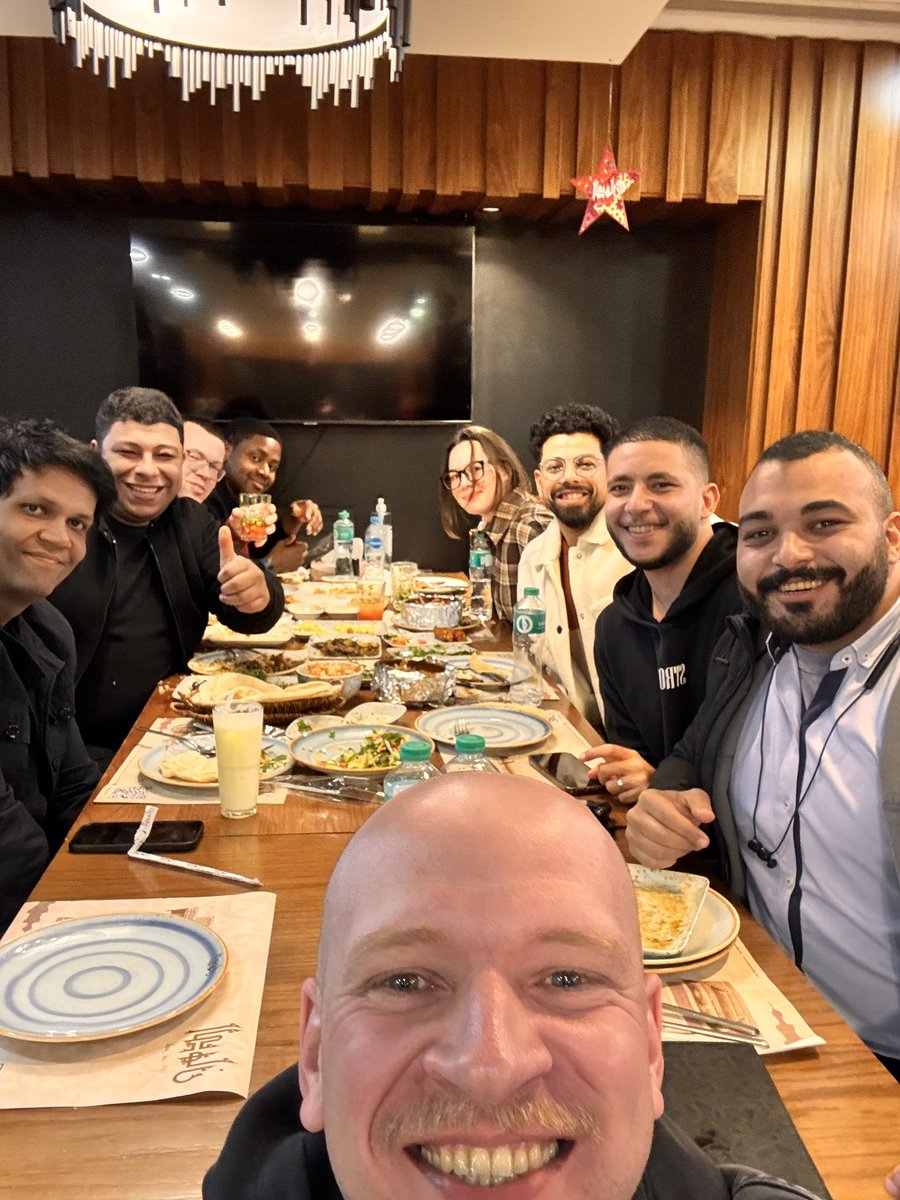

PHTalks Sao Paulo was a huge success! Results-driven cybersecurity solutions! #PHTalks My thanks to @amoshkov, the speakers, and the staff!
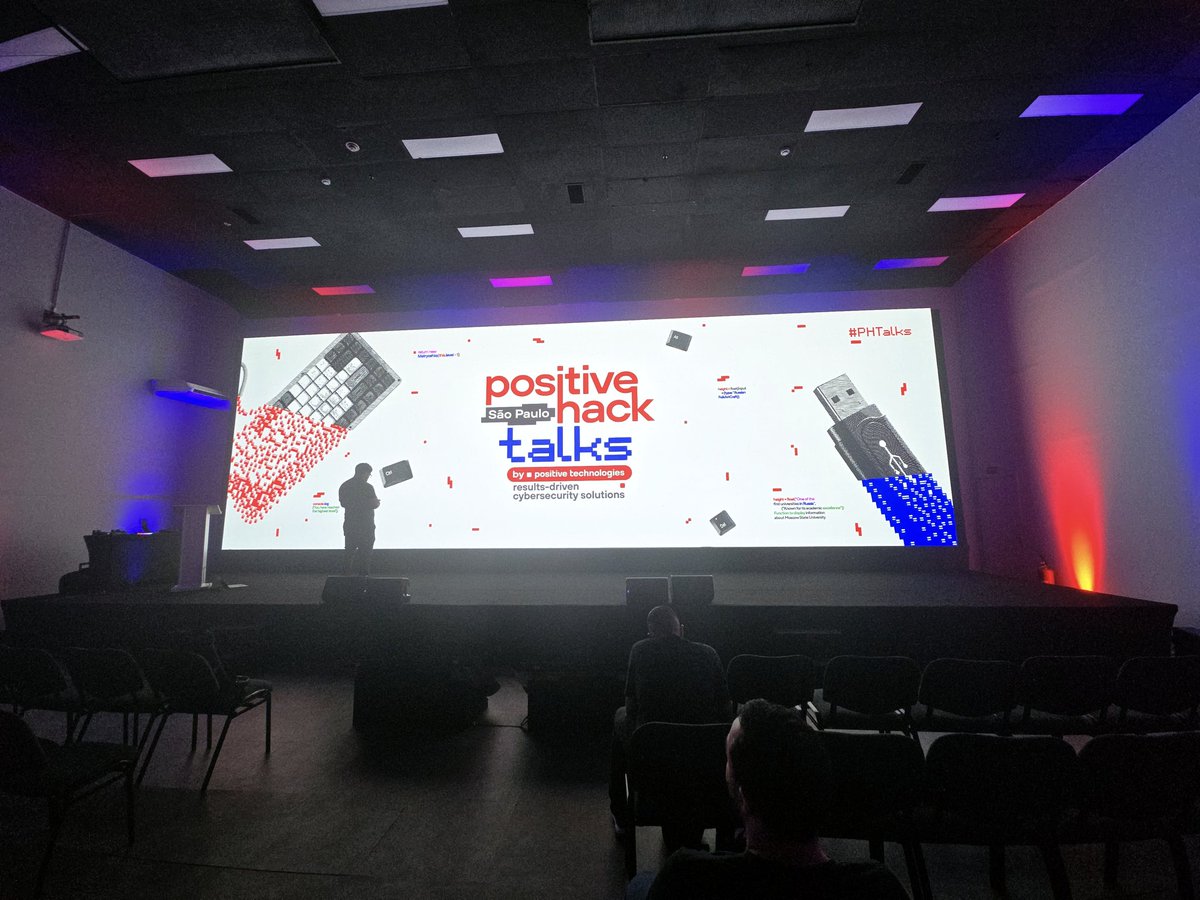

Positive Hack Talks Hanoi is go! Great turnout and awesome to finally remeet some usual suspects I haven't seen in years! #phtalks #hanoi #hackerlife #PositiveVibes
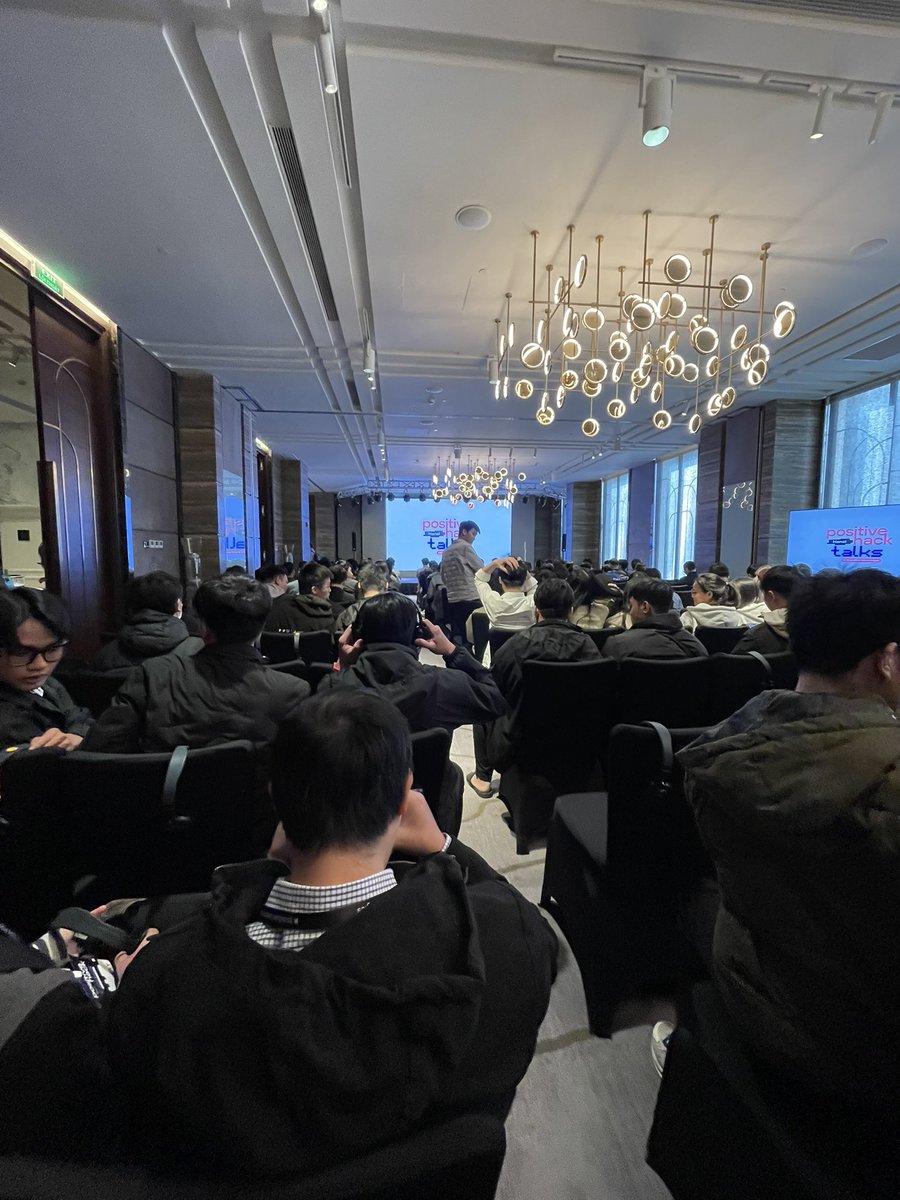

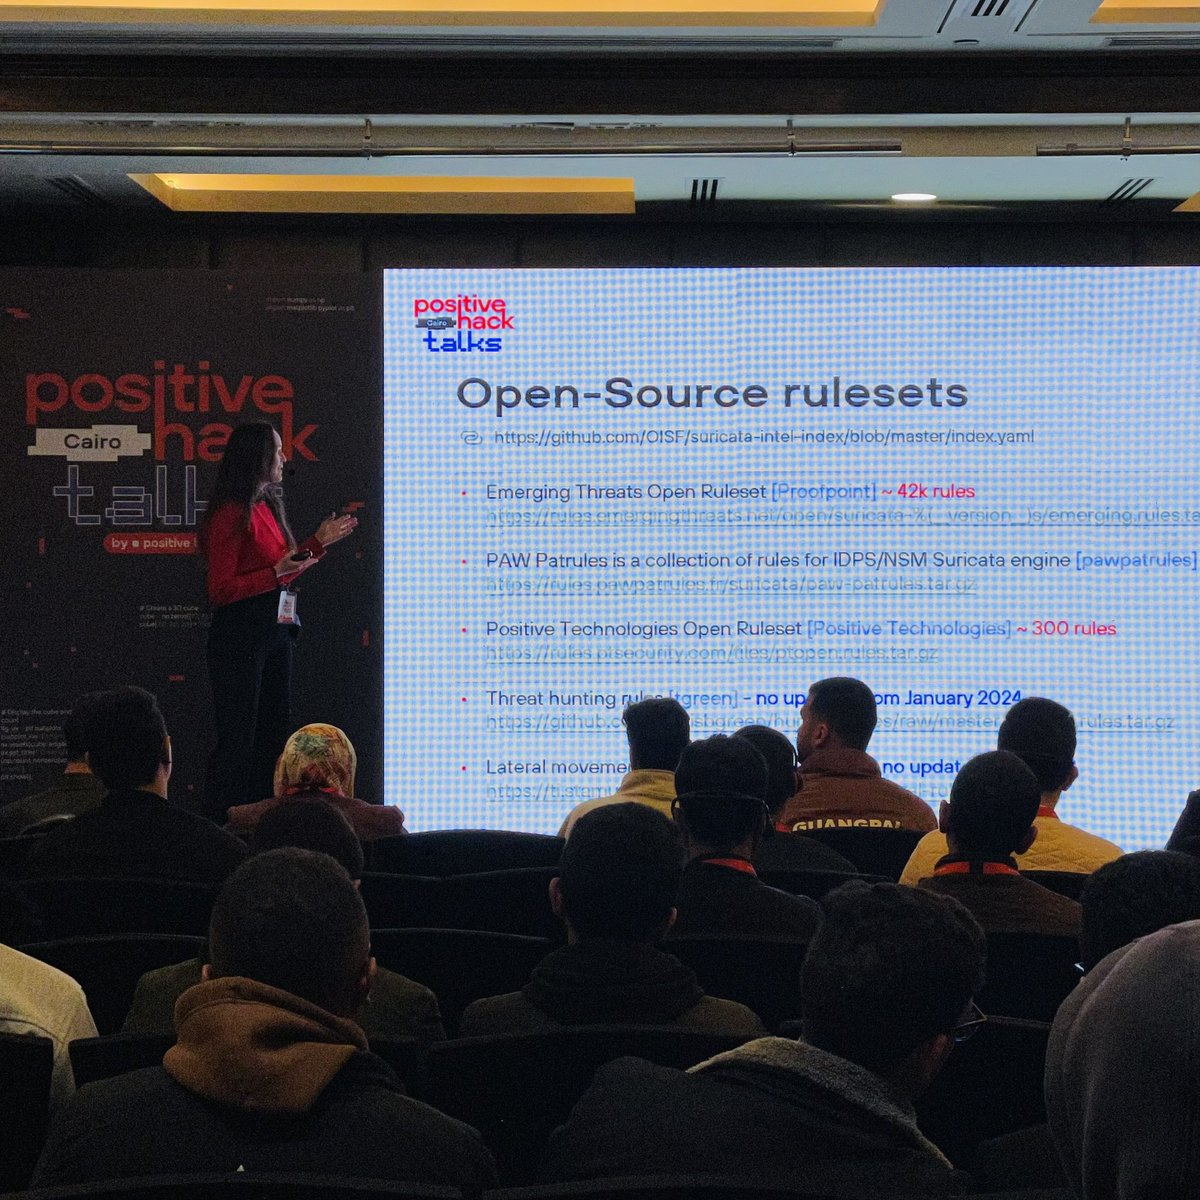
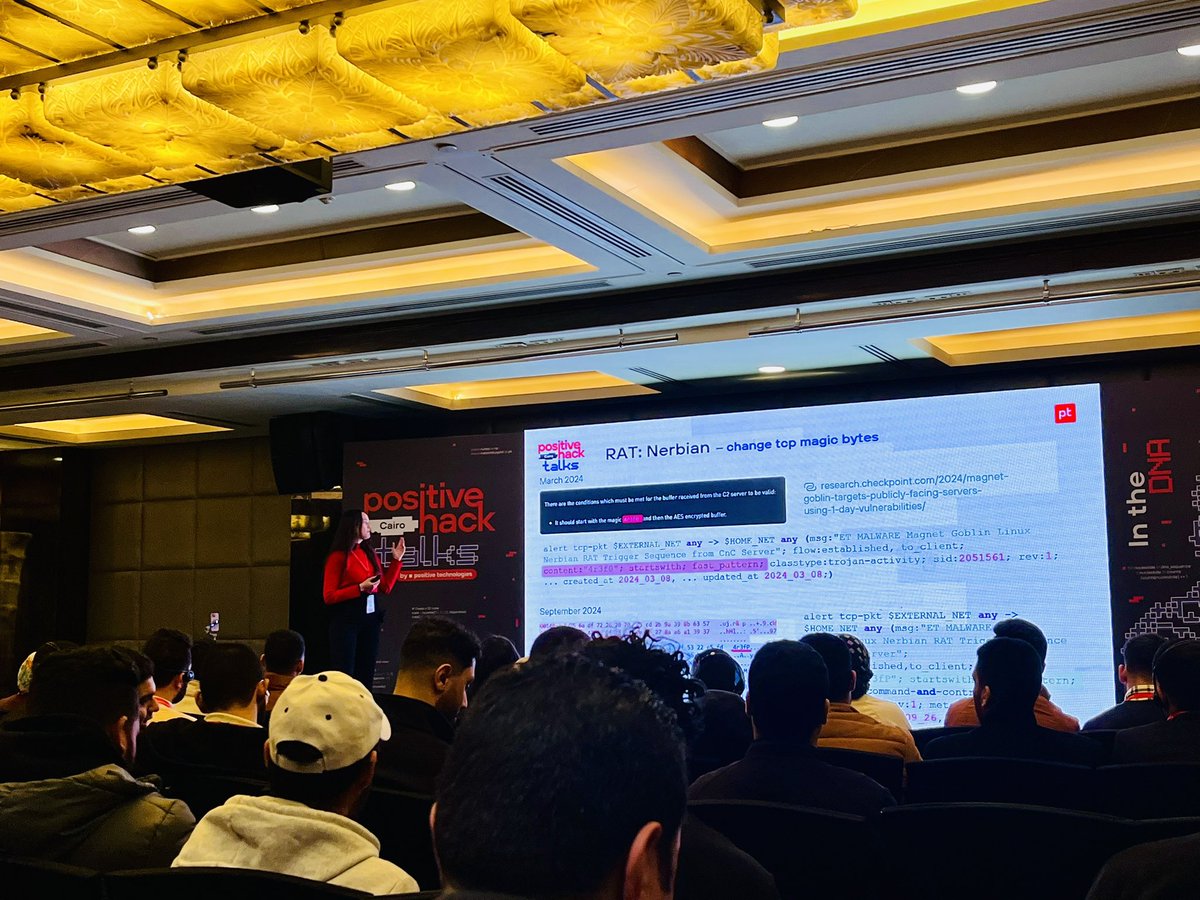
Finally have a time for tweet. This wednesday I spoke at #PHTalks in Cairo about "Effective new threat detection through generic rules in the network". I want to thank everyone who came, I'm very glad of your active participation and questions. It was a really nice trip :)

Huge thanks to the amazing team behind this incredible event! I'm truly grateful for the opportunity to learn so many new things and connect with such a vibrant, inspiring community. Can't wait for the next one! #CommunityVibes #LifelongLearning #PHTalks

Huge thanks to the organizers for an amazing event! I had a great time meeting @Zigoo0, the best in Egypt in cybersecurity, and I truly enjoyed meeting @amoshkov. Hope to see you all again soon! @PTsecurity_EN #PHTalks
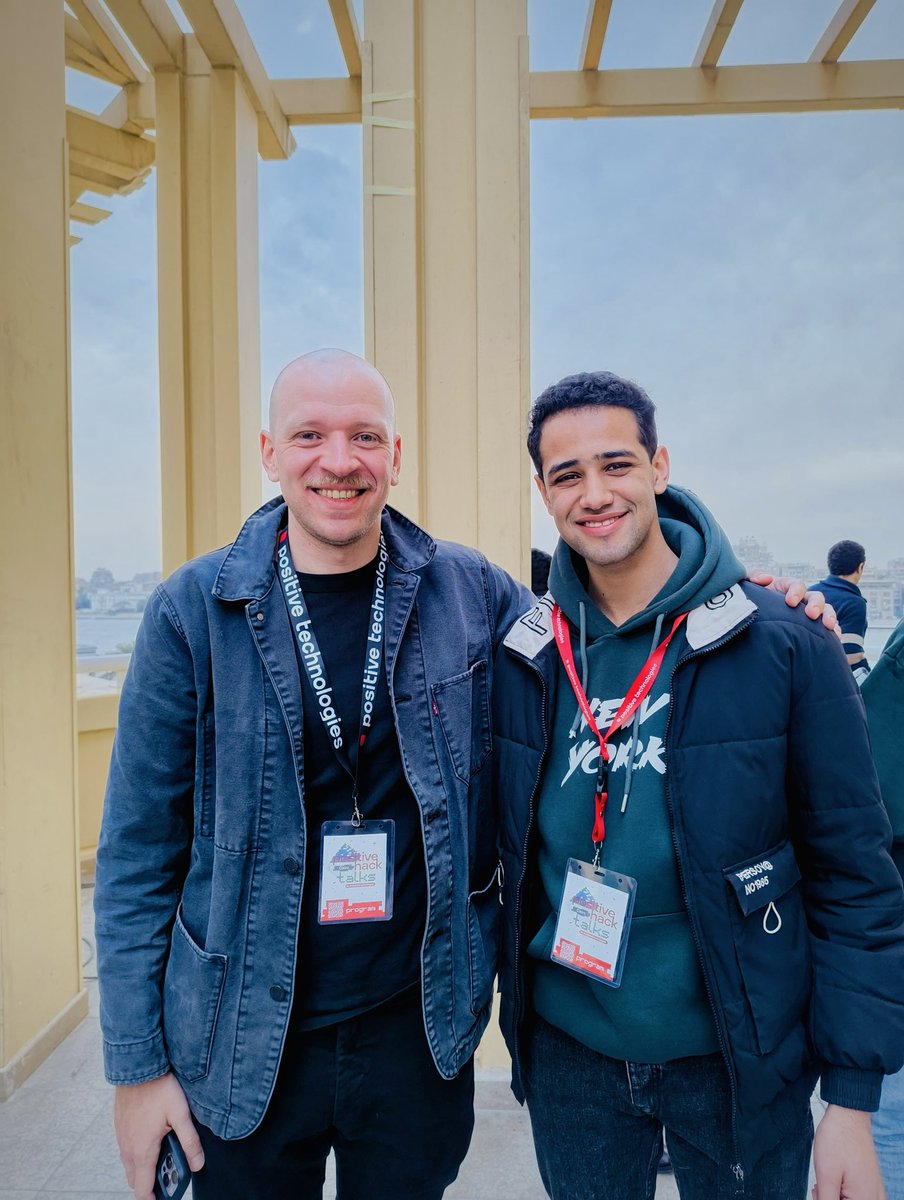

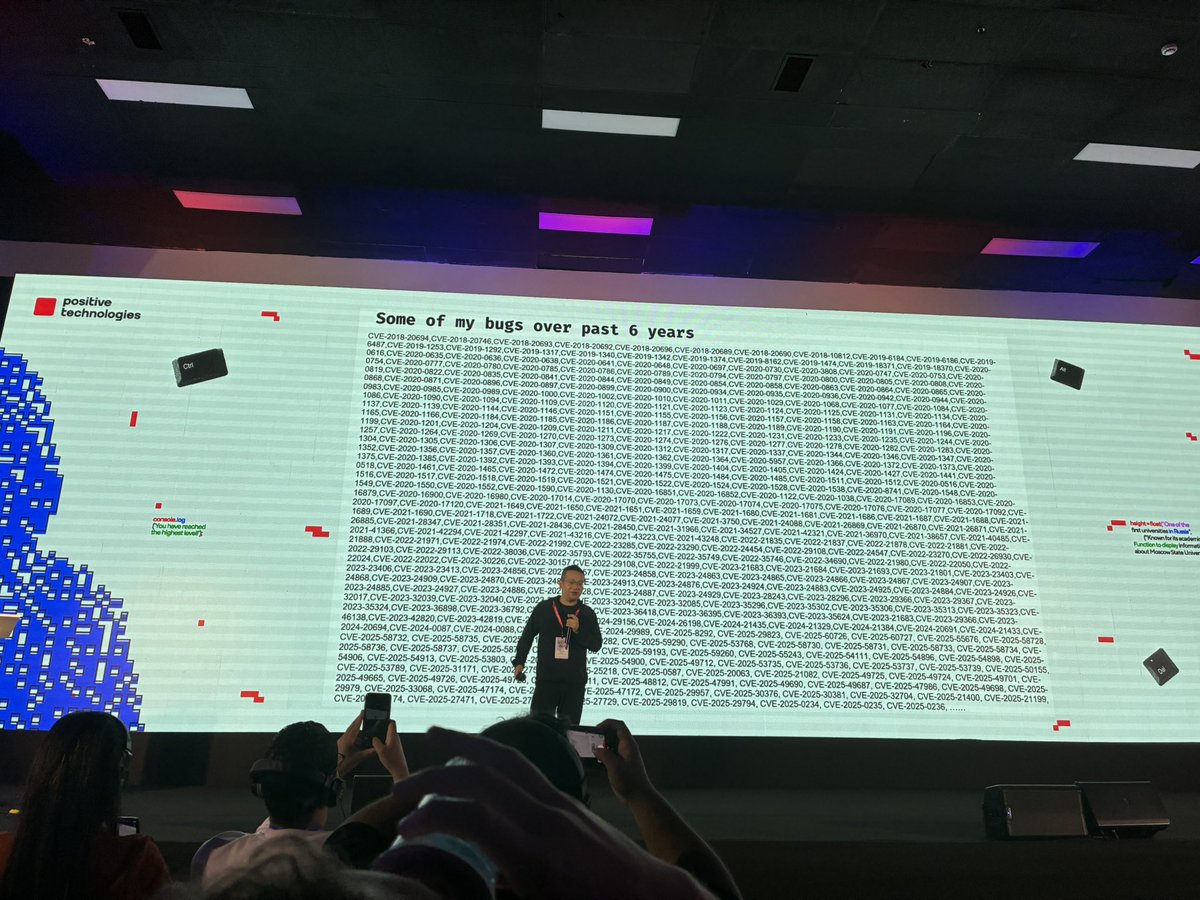
What a legend! At #PHTalks @edwardzpeng
That was the line-up. Slides and recordings are on the cards below — for the speakers who agreed to publish theirs; the rest stayed in the room.
Senior Security Consultant at Buguard
Think Like a Hacker: Out-of-the-Box Approaches to Business Logic Bugs & JS Analysis
Web Application Penetration Tester
Real-World Exploitation: Full Account Takeovers Through Client-Side Attacks
Penetration Tester at DeepStrike, LLC
The Art of Hacking GraphQL: Step-by-Step Methodology for Pentesting
Independent Bug Bounty Hunter
Cracking Java's Armor: Fuzzing the JVM for Security Weaknesses
Senior Malware Analyst at Positive Technologies
Effective new threat detection through generic rules in the network
Founder at BSides Ahmedabad
Pwned in Style: The Flashiest Hacks of All Time
Security Researcher & Lecturer at University of Applied Sciences and Arts Western Switzerland
Breaking into IoT — From Analysis to Fuzzing
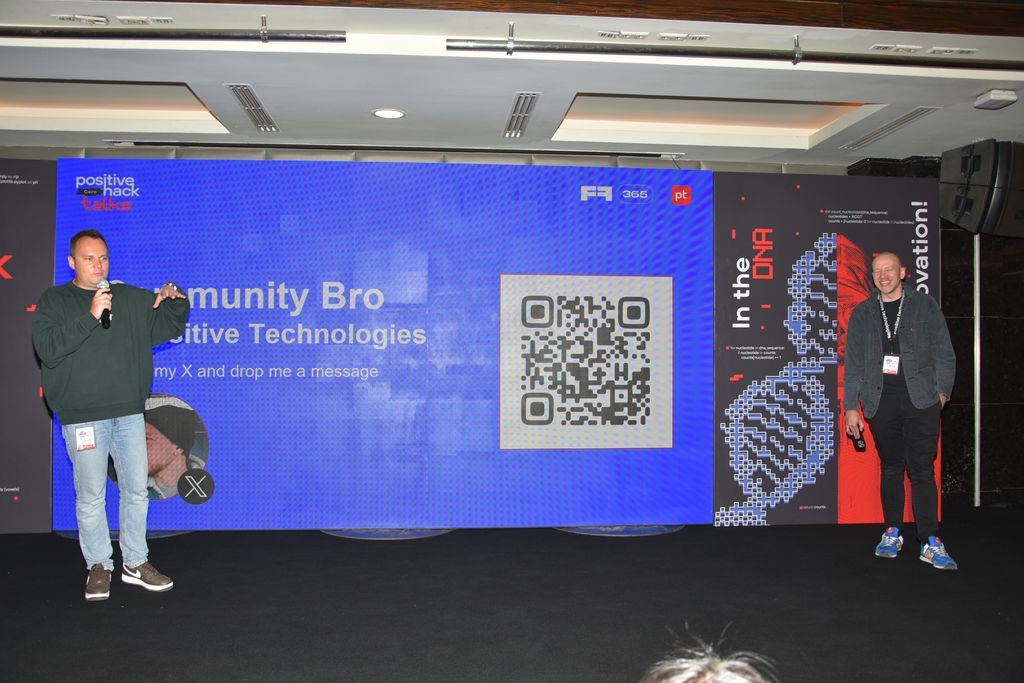
Positive Hack Talks Host
Community Bro at Positive Technologies
Thank you, Cairo! Real work on stage, hard questions from the room — that is what these stops are for. See you at the next one.
Fares Walid
Senior Security Consultant at Buguard
Nikhil Shrivastava
Founder at BSides Ahmedabad
Roland Sako
Security Researcher & Lecturer at University of Applied Sciences and Arts Western Switzerland
Kseniia Naumova
Senior Malware Analyst at Positive Technologies
Sergey Temnikov
Independent Bug Bounty Hunter
Asem Eleraky
Web Application Penetration Tester
Ahmed Qaramany
Penetration Tester at DeepStrike, LLC
Positive Technologies is an industry leader in result-driven cybersecurity and a major global provider of information security solutions. Over 4,000 organizations worldwide use technologies and services developed by our company.
In addition to developing cybersecurity products and solutions, the company organizes events and activities for everyone passionate about cybersecurity: from enthusiasts to professionals.
 PT CommunityWe build things for the security community and bring everybody together. Knowledge, tools, events, competitions — open and free for everyone.
 Positive Hack DaysAn international cyberfestival for those who want to dive into the world of cybersecurity and have a great time.
 Positive Hack CampAnnual international event for cybersecurity beginners from around the globe to gain insights from leading specialists in IT infrastructure protection and cybersecurity.
 Cybersecurity calendarEvery conference, CFP and meetup — in one place.
 @ptswarmWhere the Positive Technologies Offensive Team shares their latest findings, exploits, and deep-technical write-ups.
 dbu.gsThe most complete and up-to-date vulnerability database with researcher profiles, AI summaries, and trending analysis.
 Standoff Bug BountyA bug bounty platform with generous rewards for discovering vulnerabilities in top companies.