

Alex Moshkov
@amoshkov
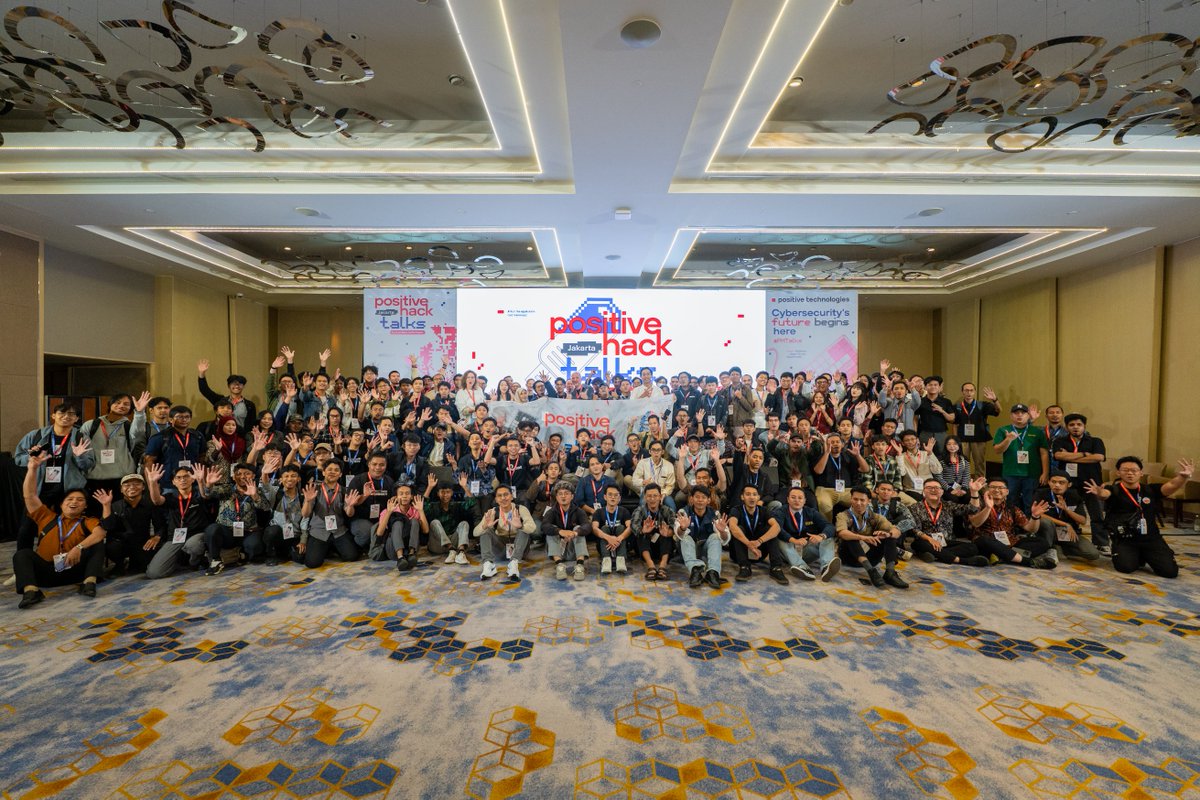
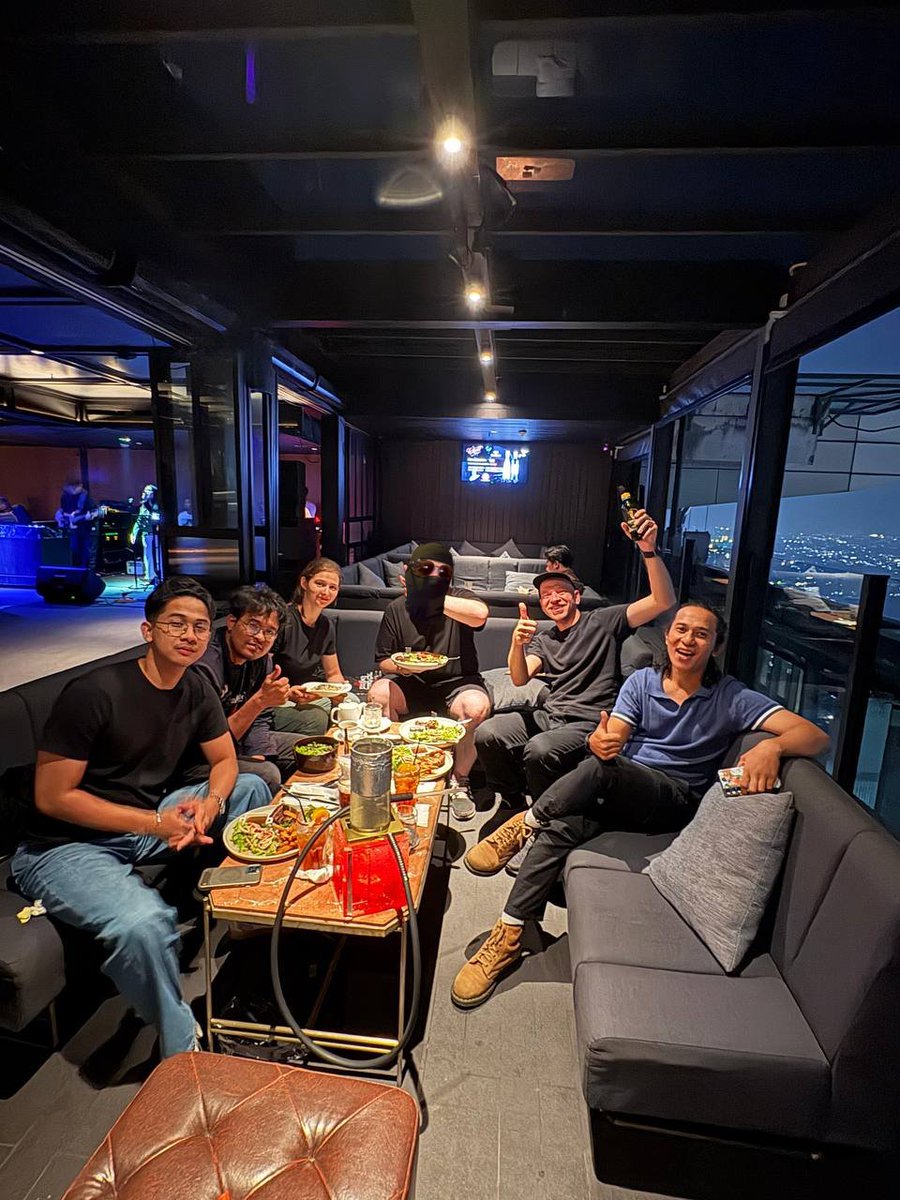
Another legendary shot from #PHTalks Jakarta — keeping this as a tradition for every next con! Unbelievable — 370+ attendees, a record for all past talks. And this photo shows just a part of them.
A free, community-driven cybersecurity conference where real hackers share what they've built, broken, and learned. No marketing, no nonsense. Brutally honest — just the way it should be.
A free, community-driven cybersecurity conference where real hackers share what they've built, broken, and learned. No marketing, no nonsense. Brutally honest — just the way it should be.
This stop took place on May 5, 2026.
Next stop: Goa, December 10, 2026 →Bug bounty, pentest, red team, OSINT. Real techniques, not theory.
Real cases — and how the vulns were actually found.
Grill the speakers. Answers you won't get from a blog.
Meet people who actually break things. No badge-scanning.
Another legendary shot from #PHTalks Jakarta — keeping this as a tradition for every next con! Unbelievable — 370+ attendees, a record for all past talks. And this photo shows just a part of them.

370+ #cybersecurity pros. 8 amazing talks by @cnwatcher @shipcod3 @pyn3rd @nalen98 @ElementalX2 @BukanYahya 1 epic #PHTalks Jakarta From car hacking to AI-powered detections — we brought it all Slides & Photos: https://t.co/4UZX2BQXI0 Share highlights and tag #PHTalks

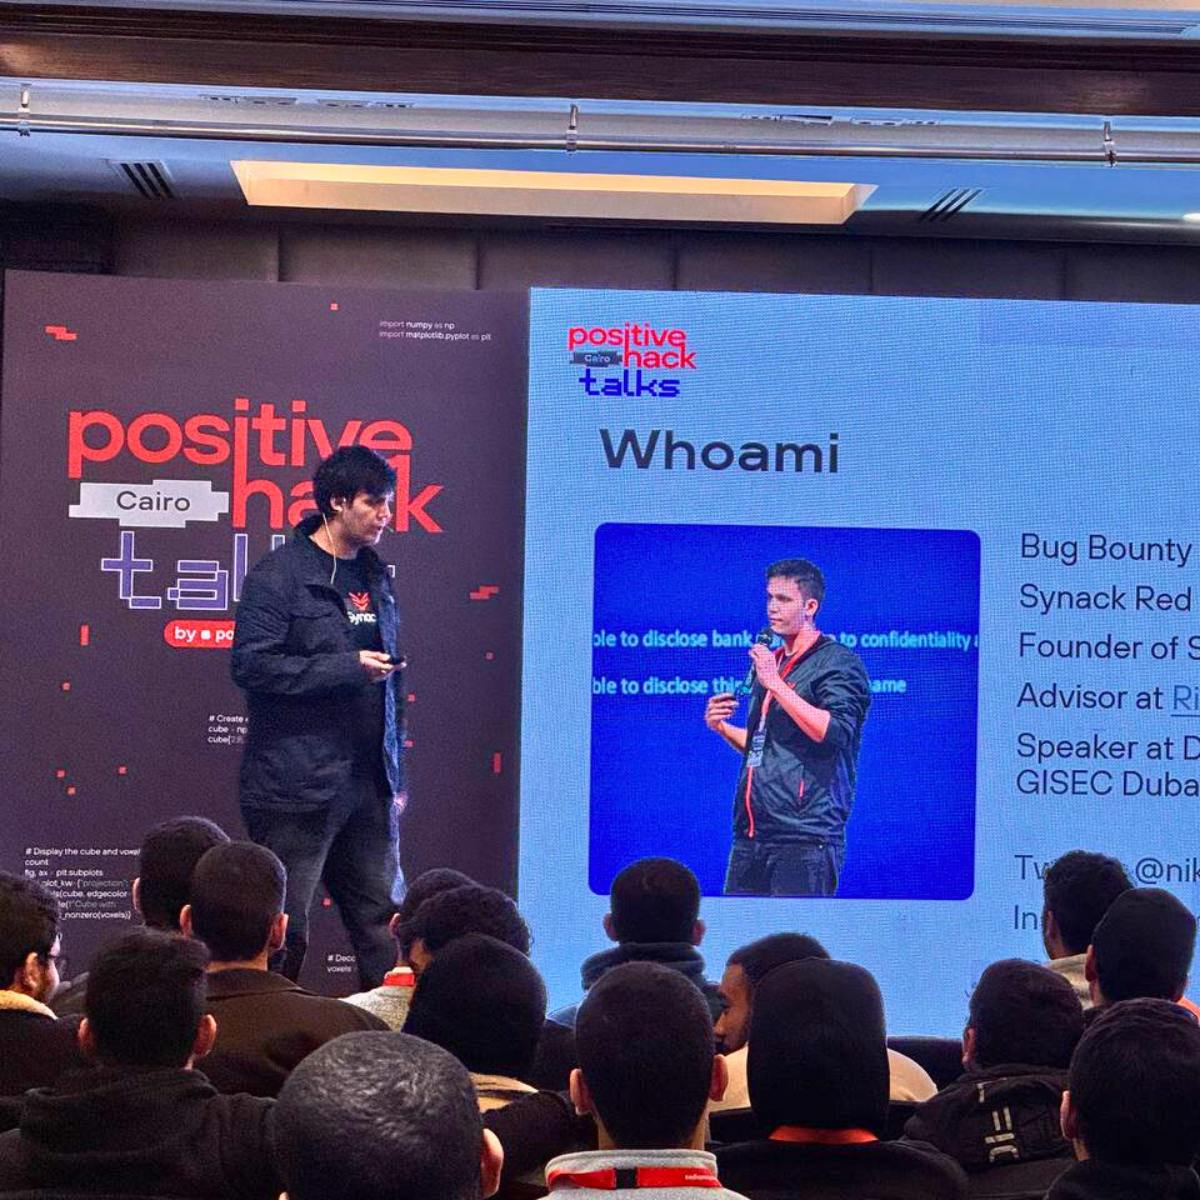
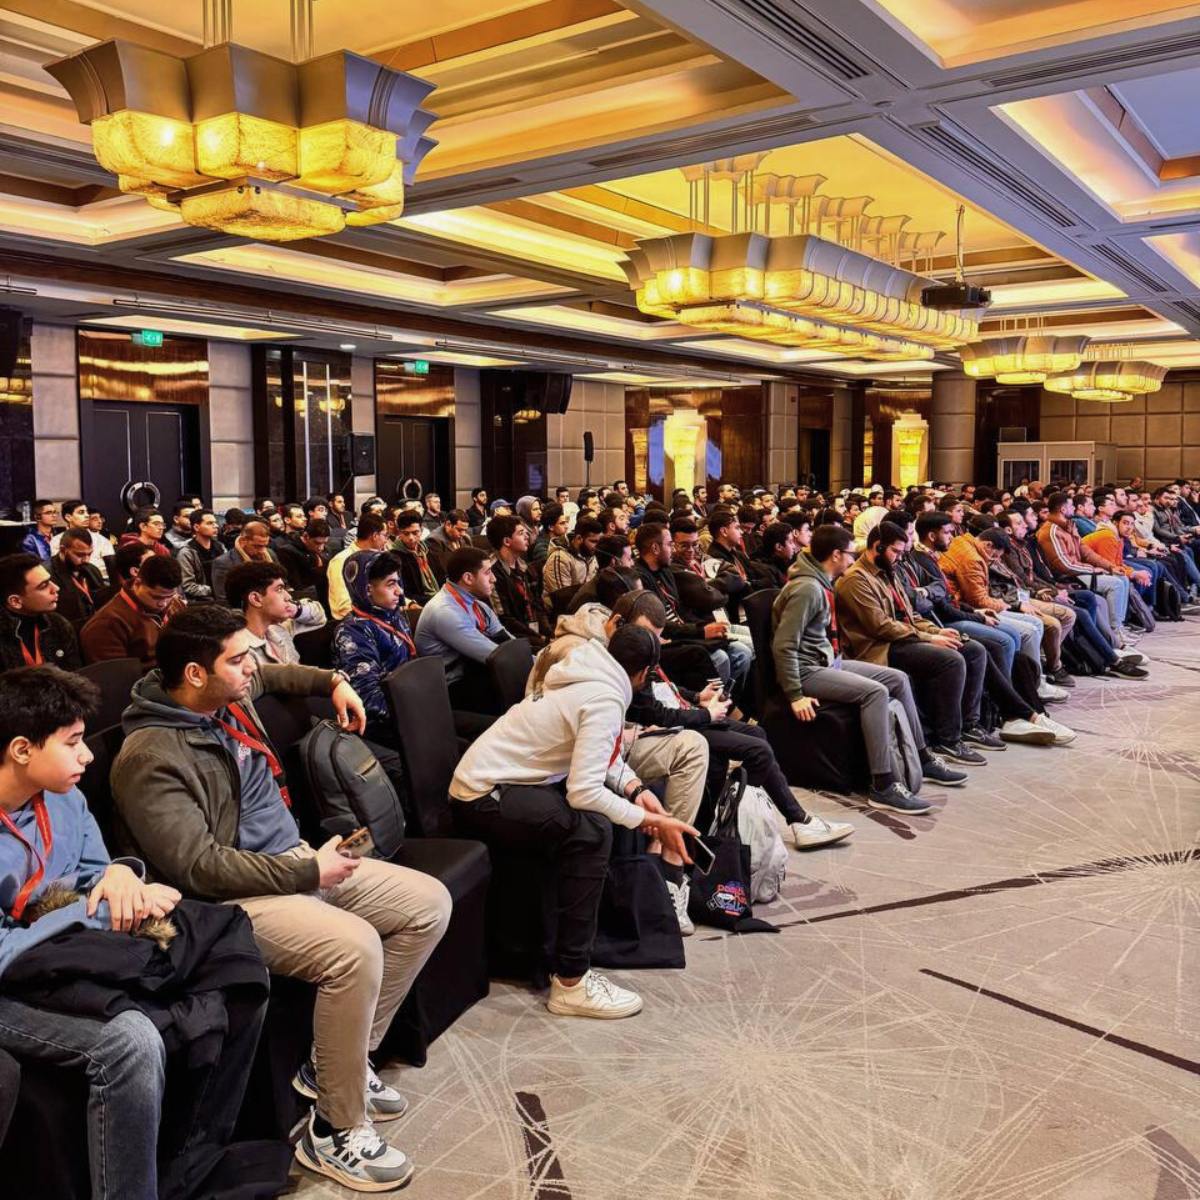
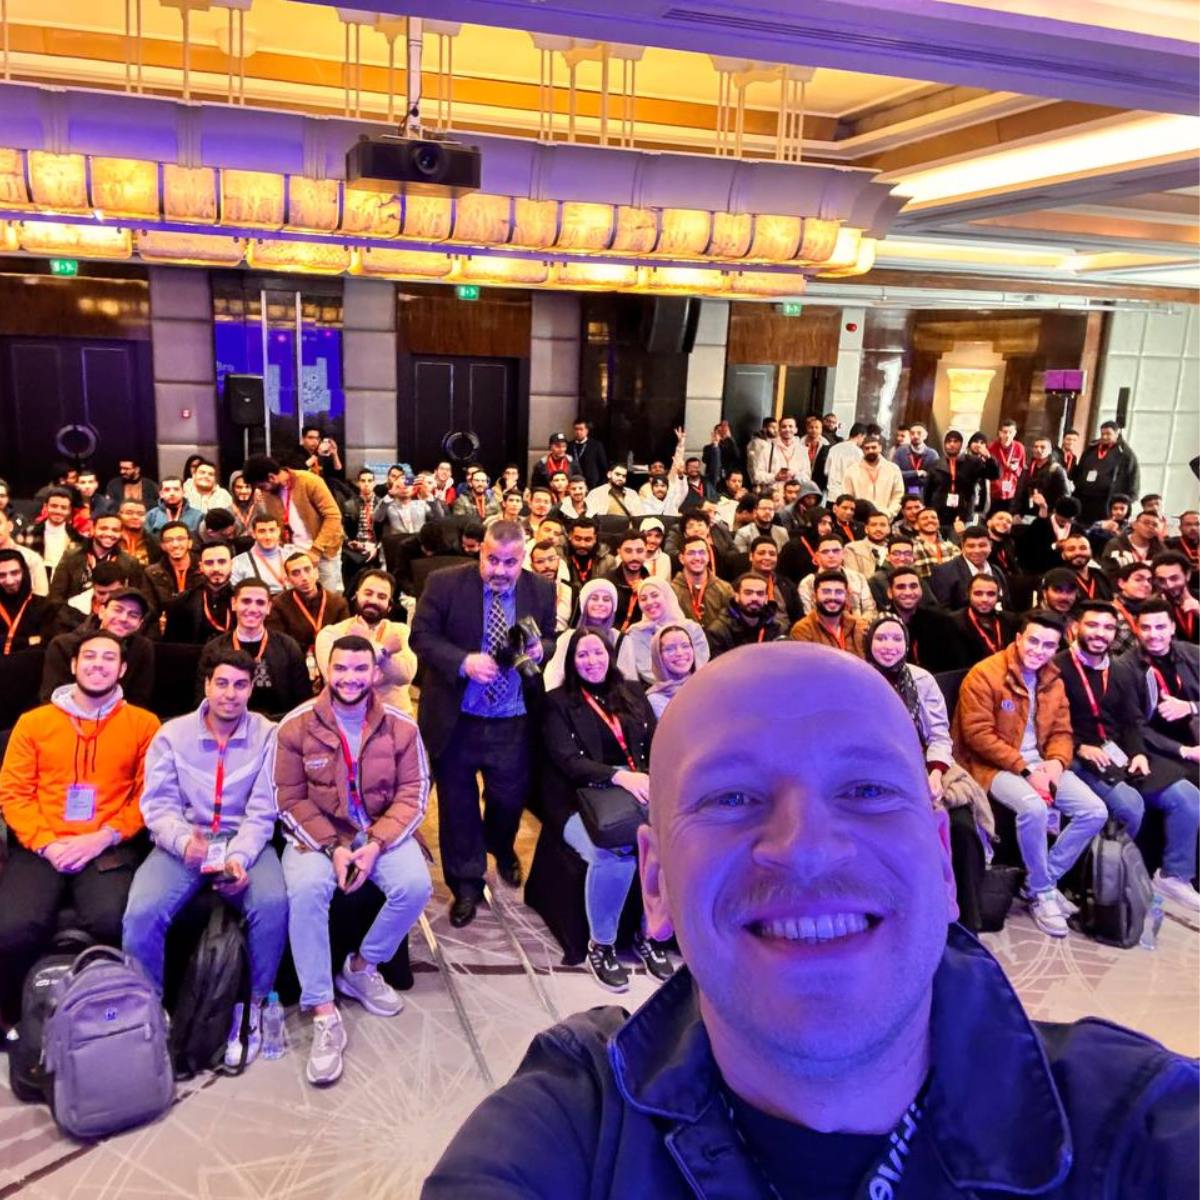
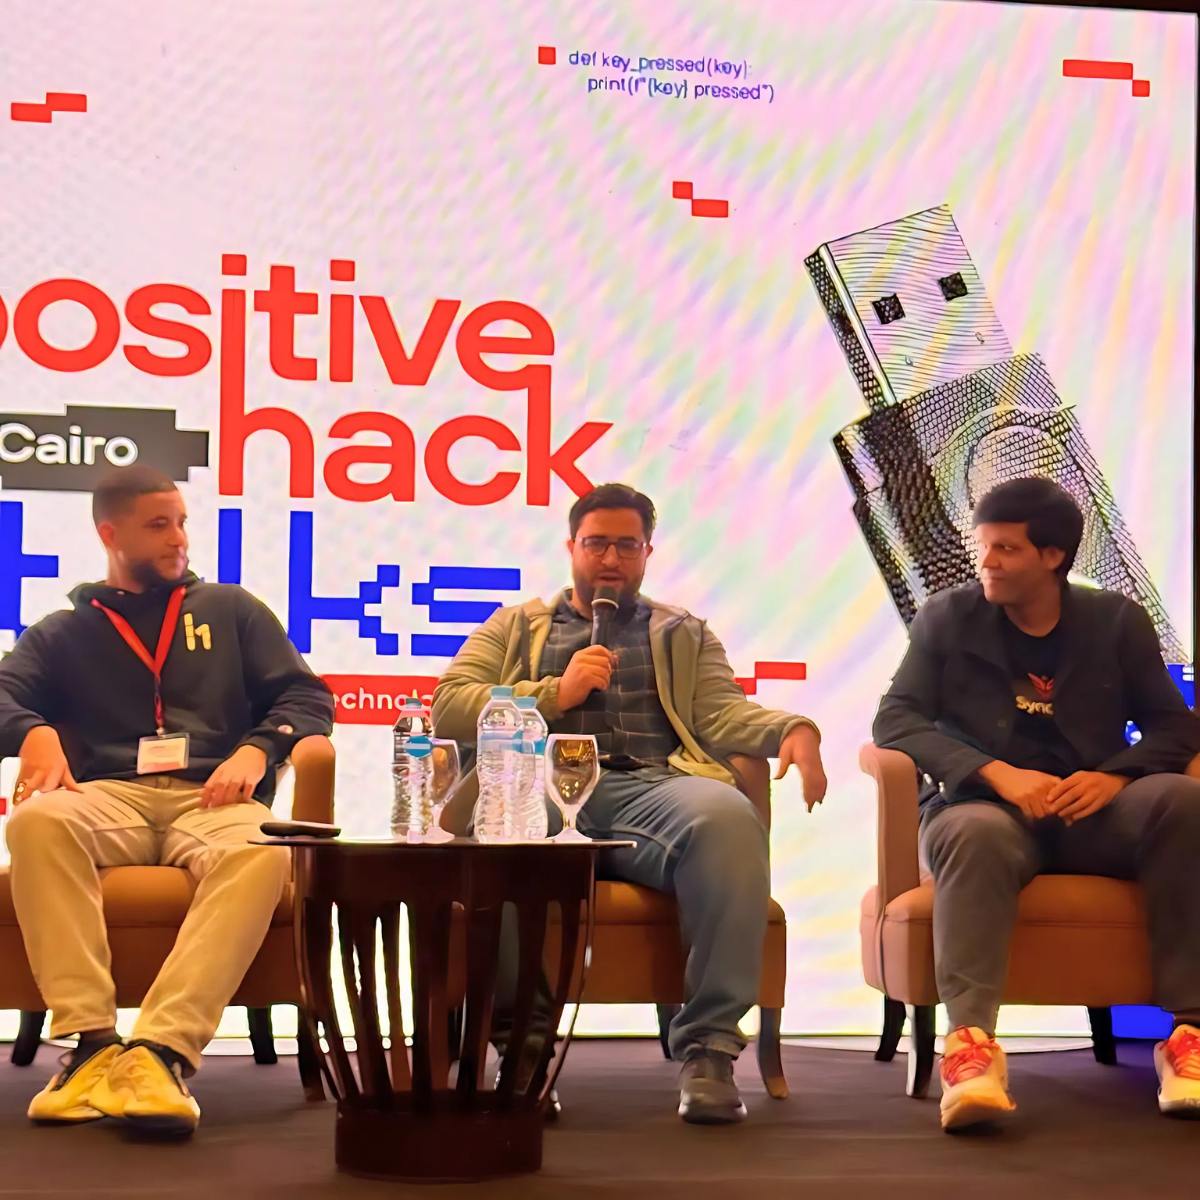
#PHTalks landed in Cairo, Egypt On February 26, the event brought together 200+ hackers for an intense exchange of ideas. An in-person meetup for cybersecurity specialists ready to absorb the latest knowledge on offensive and defensive security and bug hunting.
Thanks, Hanoi! Over 200 cybersecurity pros joined Positive Hack Talks for expert insights, hot topics, and great networking. From bug hunting to tackling top threats, it was a day to remember. Shoutout to our speakers! See you next time! #Cybersecurity #PHTalks
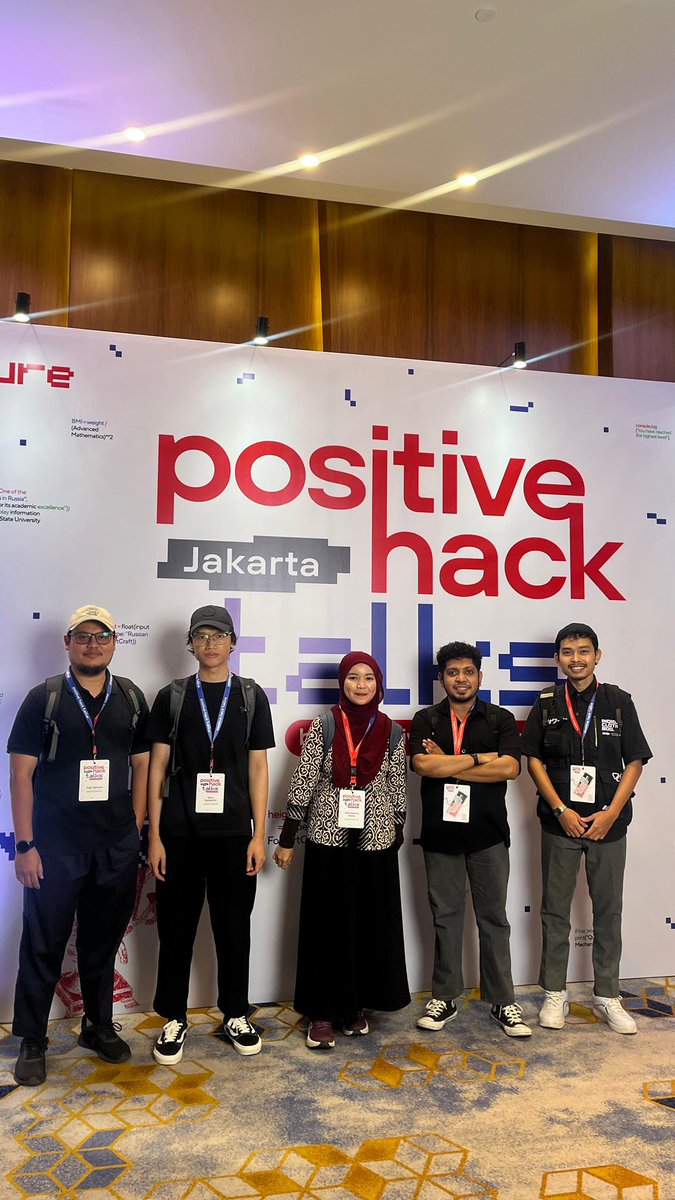
Idk guys — @nizarakbarm @Nalen98 @shipcod3 @BukanYahya @screetsec @ElementalX2 — not sure how it happened, but we've got no proper group photo together from #PHTalks Jakarta. So here's what I managed to collect
An incredible experience before the #PHTalks. Thank you all so much!!@SirBagoza @niksthehacker @naumovax @rosako @amoshkov @0xMalWan @Ellord0Xd @m359ah @SergeyTemnikov2

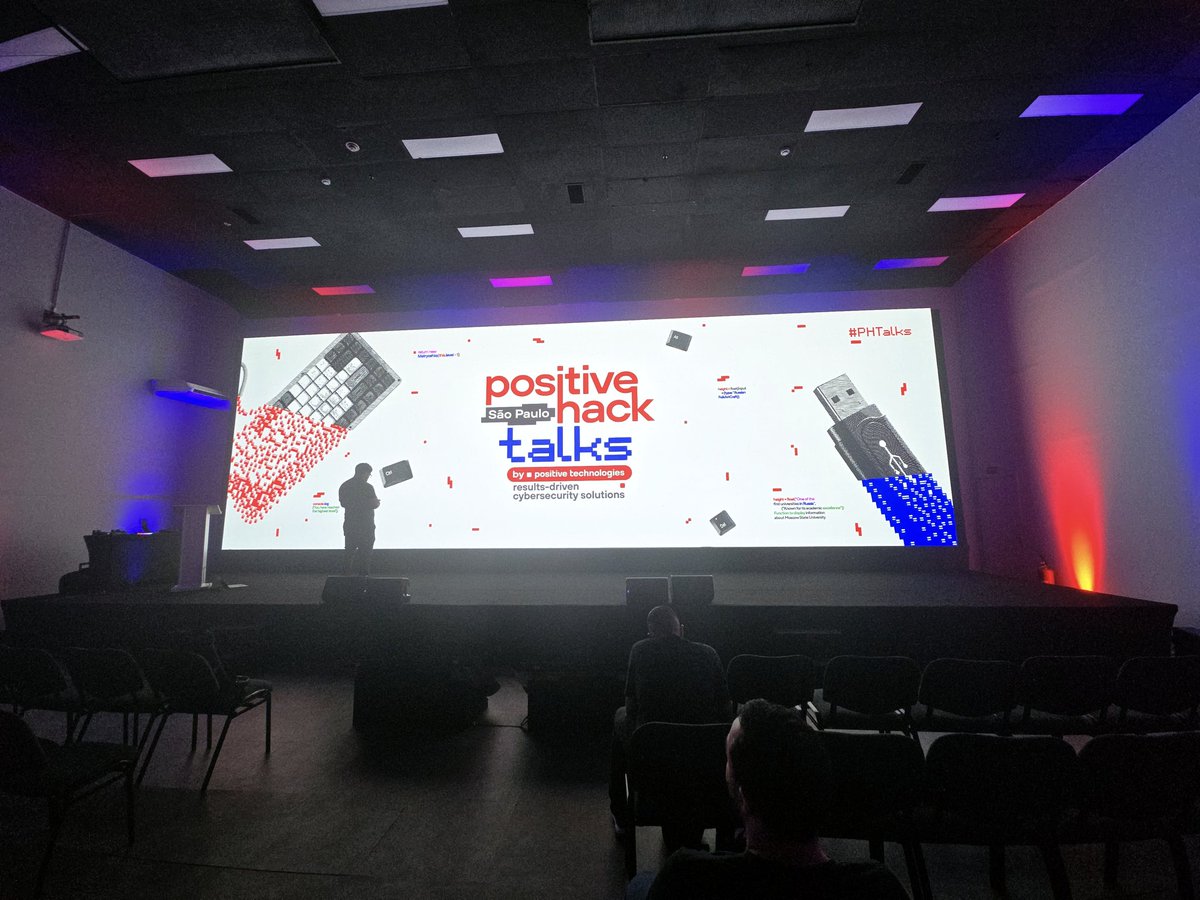
PHTalks Sao Paulo was a huge success! Results-driven cybersecurity solutions! #PHTalks My thanks to @amoshkov, the speakers, and the staff!

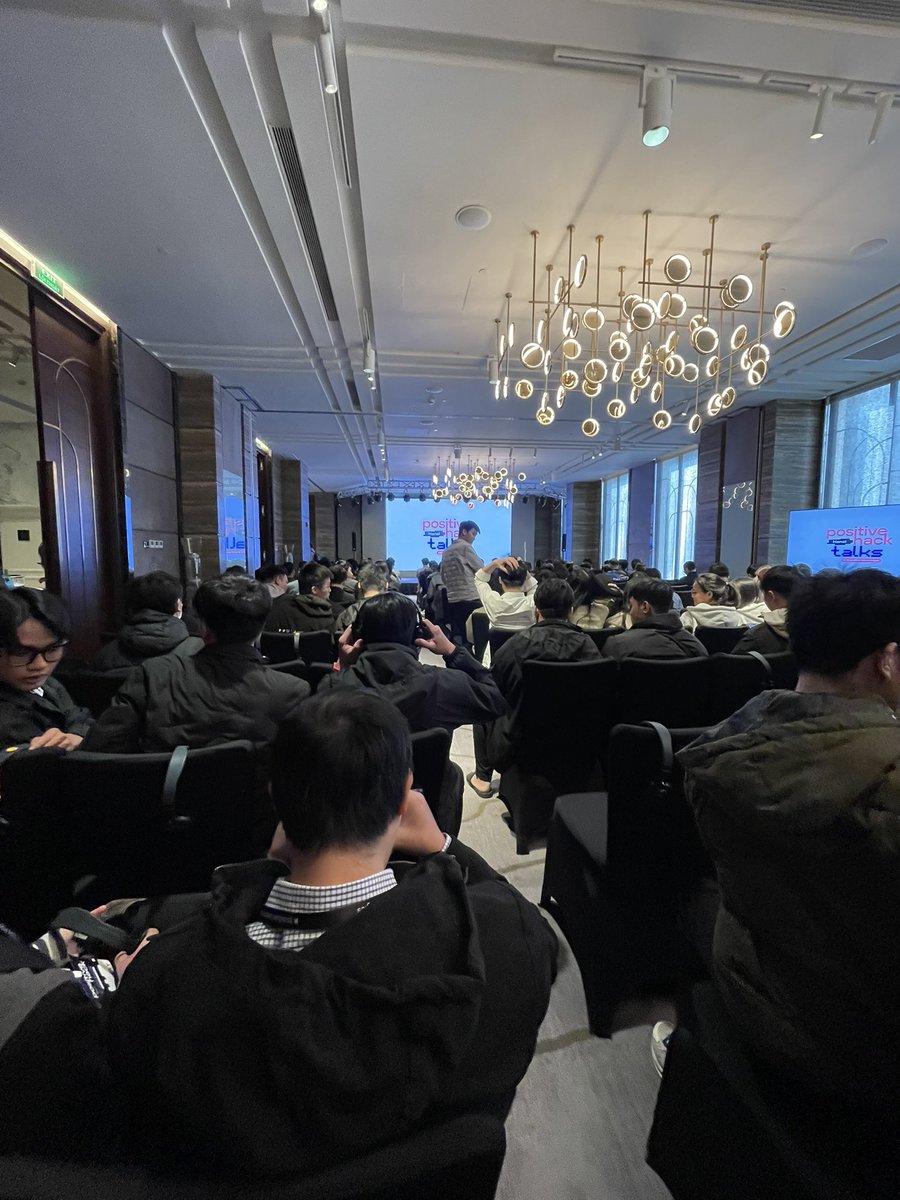
Positive Hack Talks Hanoi is go! Great turnout and awesome to finally remeet some usual suspects I haven't seen in years! #phtalks #hanoi #hackerlife #PositiveVibes

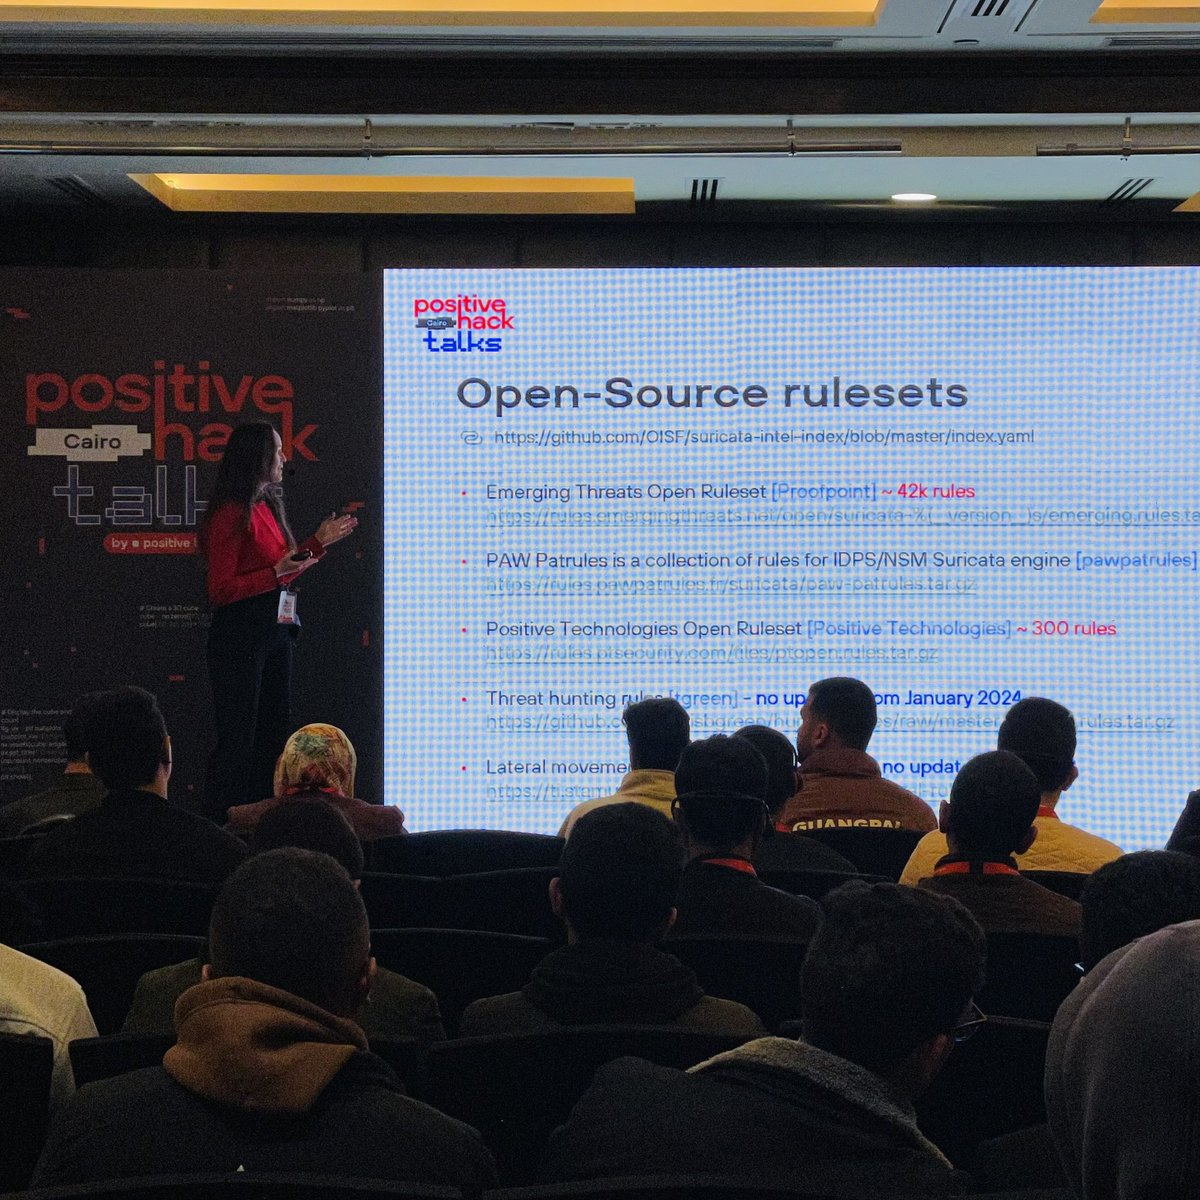
Finally have a time for tweet. This wednesday I spoke at #PHTalks in Cairo about "Effective new threat detection through generic rules in the network". I want to thank everyone who came, I'm very glad of your active participation and questions. It was a really nice trip :)

Huge thanks to the amazing team behind this incredible event! I'm truly grateful for the opportunity to learn so many new things and connect with such a vibrant, inspiring community. Can't wait for the next one! #CommunityVibes #LifelongLearning #PHTalks

Huge thanks to the organizers for an amazing event! I had a great time meeting @Zigoo0, the best in Egypt in cybersecurity, and I truly enjoyed meeting @amoshkov. Hope to see you all again soon! @PTsecurity_EN #PHTalks
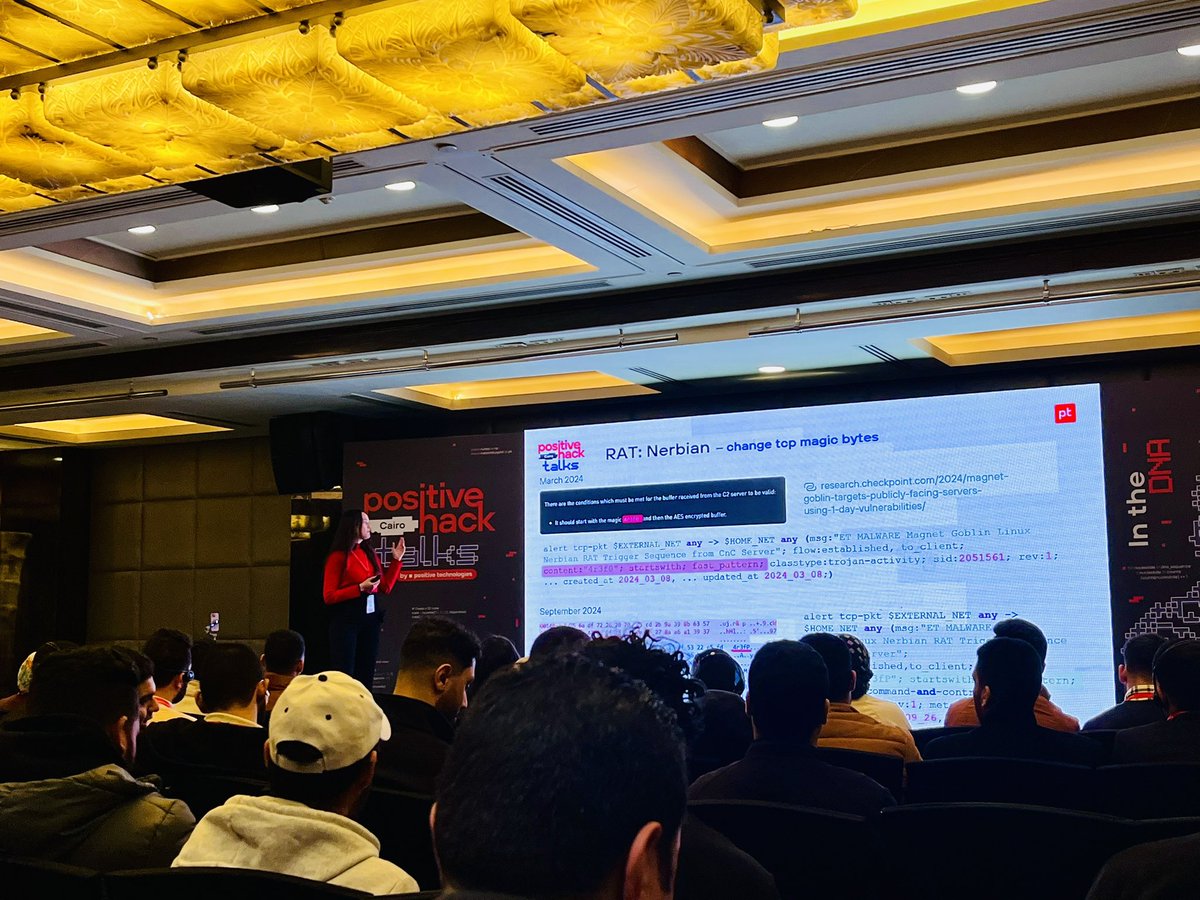

What a legend! At #PHTalks @edwardzpeng
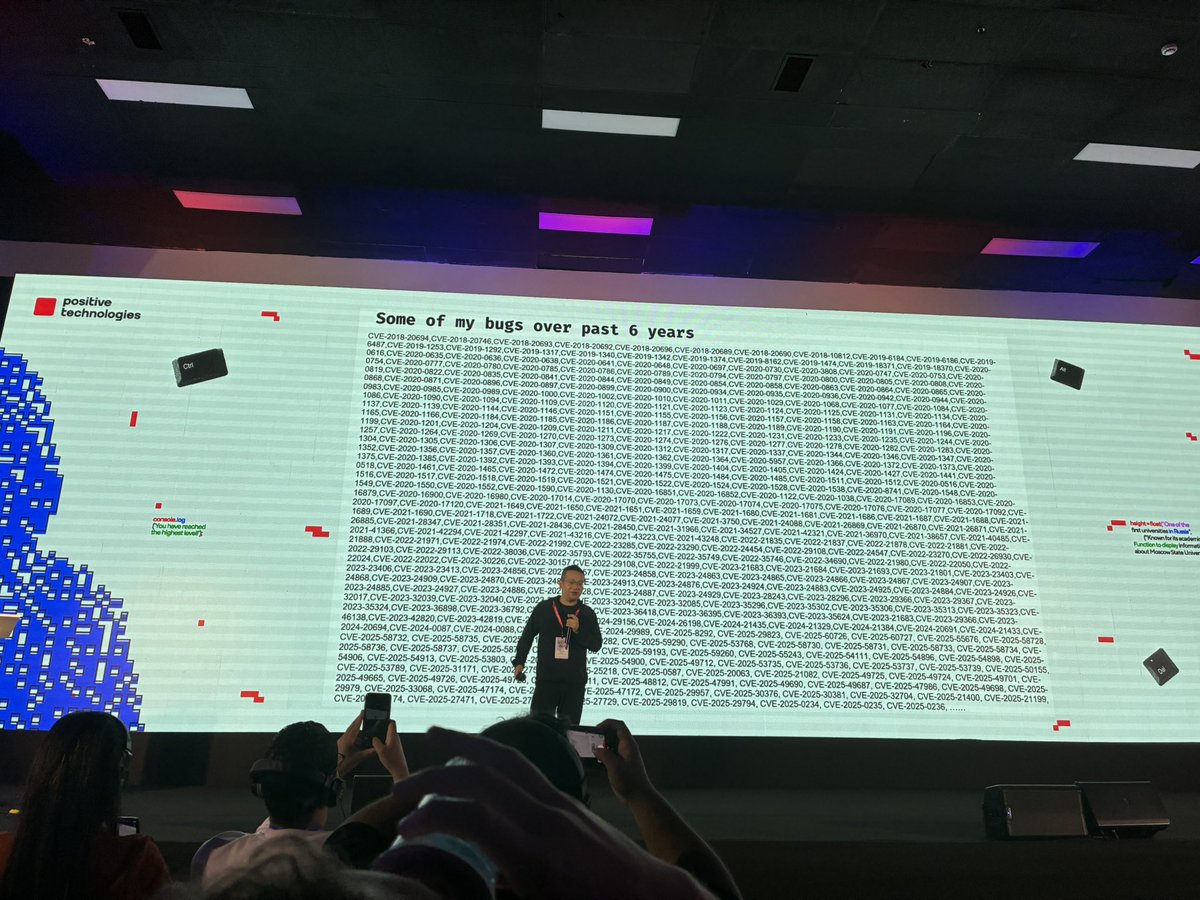
That was the line-up. Slides and recordings are on the cards below — for the speakers who agreed to publish theirs; the rest stayed in the room.
Linux Kernel Developer and Security Researcher at Positive Technologies
Kernel-Hack-Drill Masterclass
Security Researcher & Bug Bounty Hunter
Send a Fax as Anyone, Upload Photos to Any Frame: The Hidden Risks of Authorization in Email-Driven Systems
Security Analyst (Offensive)
Spray, Pray, Validate: Lessons from AI-assisted Vulnerability Research
Senior Security Researcher at Siemens Healthineers
Trojan Penguin in the Windows: Advanced Attack Vectors Through WSL
Application Security Specialist at Kaspersky
PhantomRPC: A New Privilege Escalation Flaw in Windows RPC
Security Researcher at ONESEC
Kernel Wars: Anti-Cheat Reversing, BYOVD Exploitation and Mitigations
Senior Product Security Engineer
Dissecting Android RASP: A Practical Reversing Guide
Independent Cybersecurity and OSINT Researcher · Senior Information Security Analyst & OSINT Researcher
Dead in the Water: Tracking Ships Through VSAT When AIS Goes Dark
That was the community half of the day. Where a speaker agreed to publish, their slides and recording are on the card.
Founder, I/O TRIX
Building Malaysia's OT/IoT Cybersecurity Future
Lead Agent MCC & Security Researcher
Breaking the Gatekeepers: How We Sparked Malaysia's New Cyber Talent Movement
Security Analyst
Free for all: Curated Threat Intelligence Feed with relevancy to Malaysian Threat Landscape
Positive Hack Talks Host
Community Bro at Positive Technologies
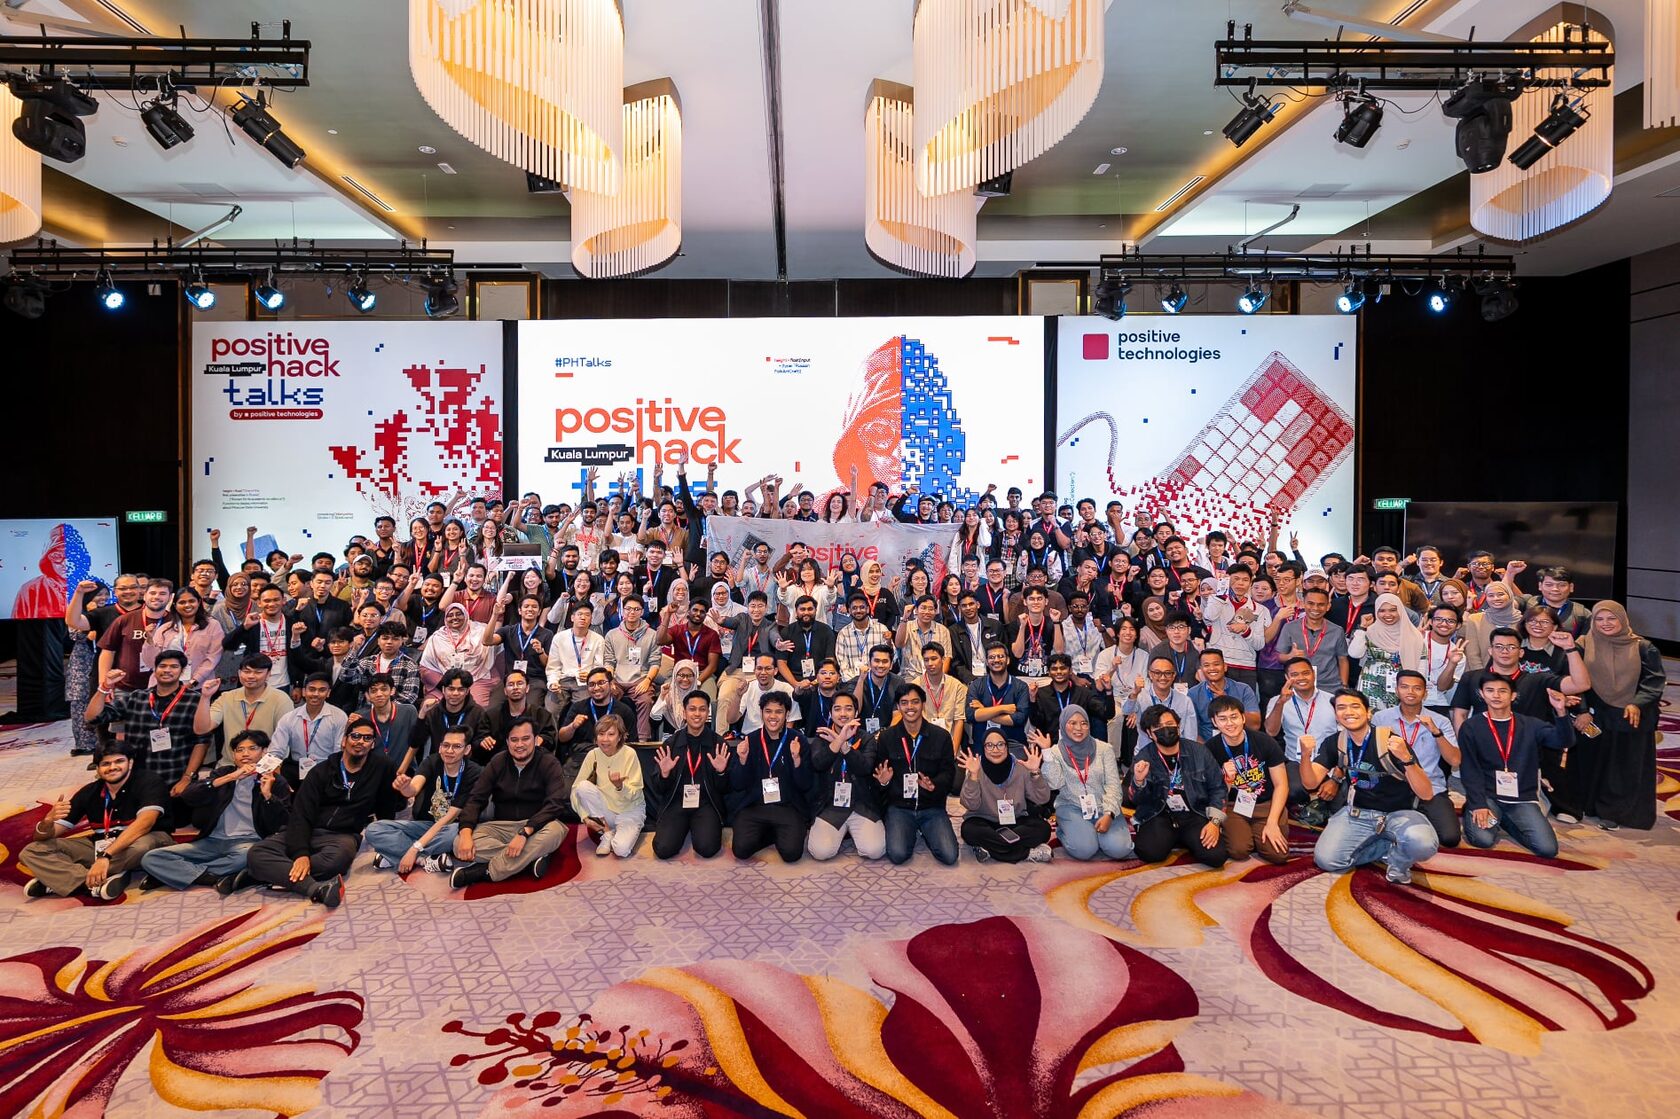
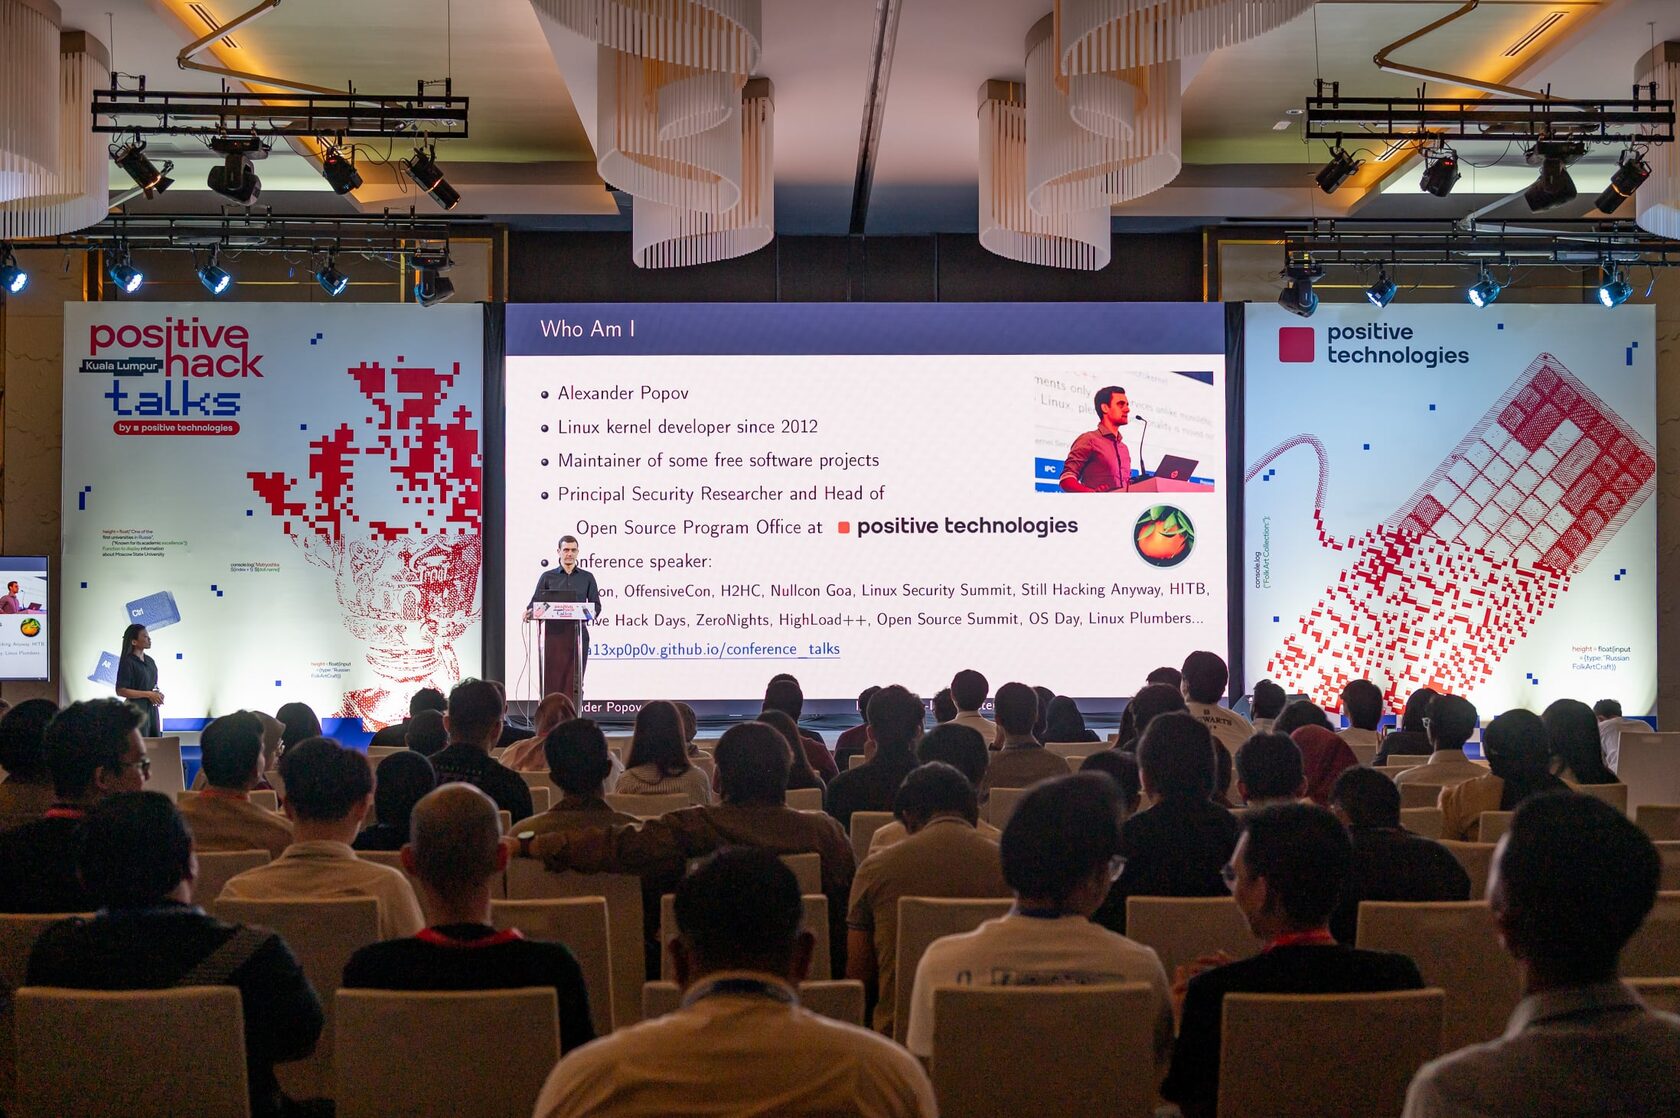
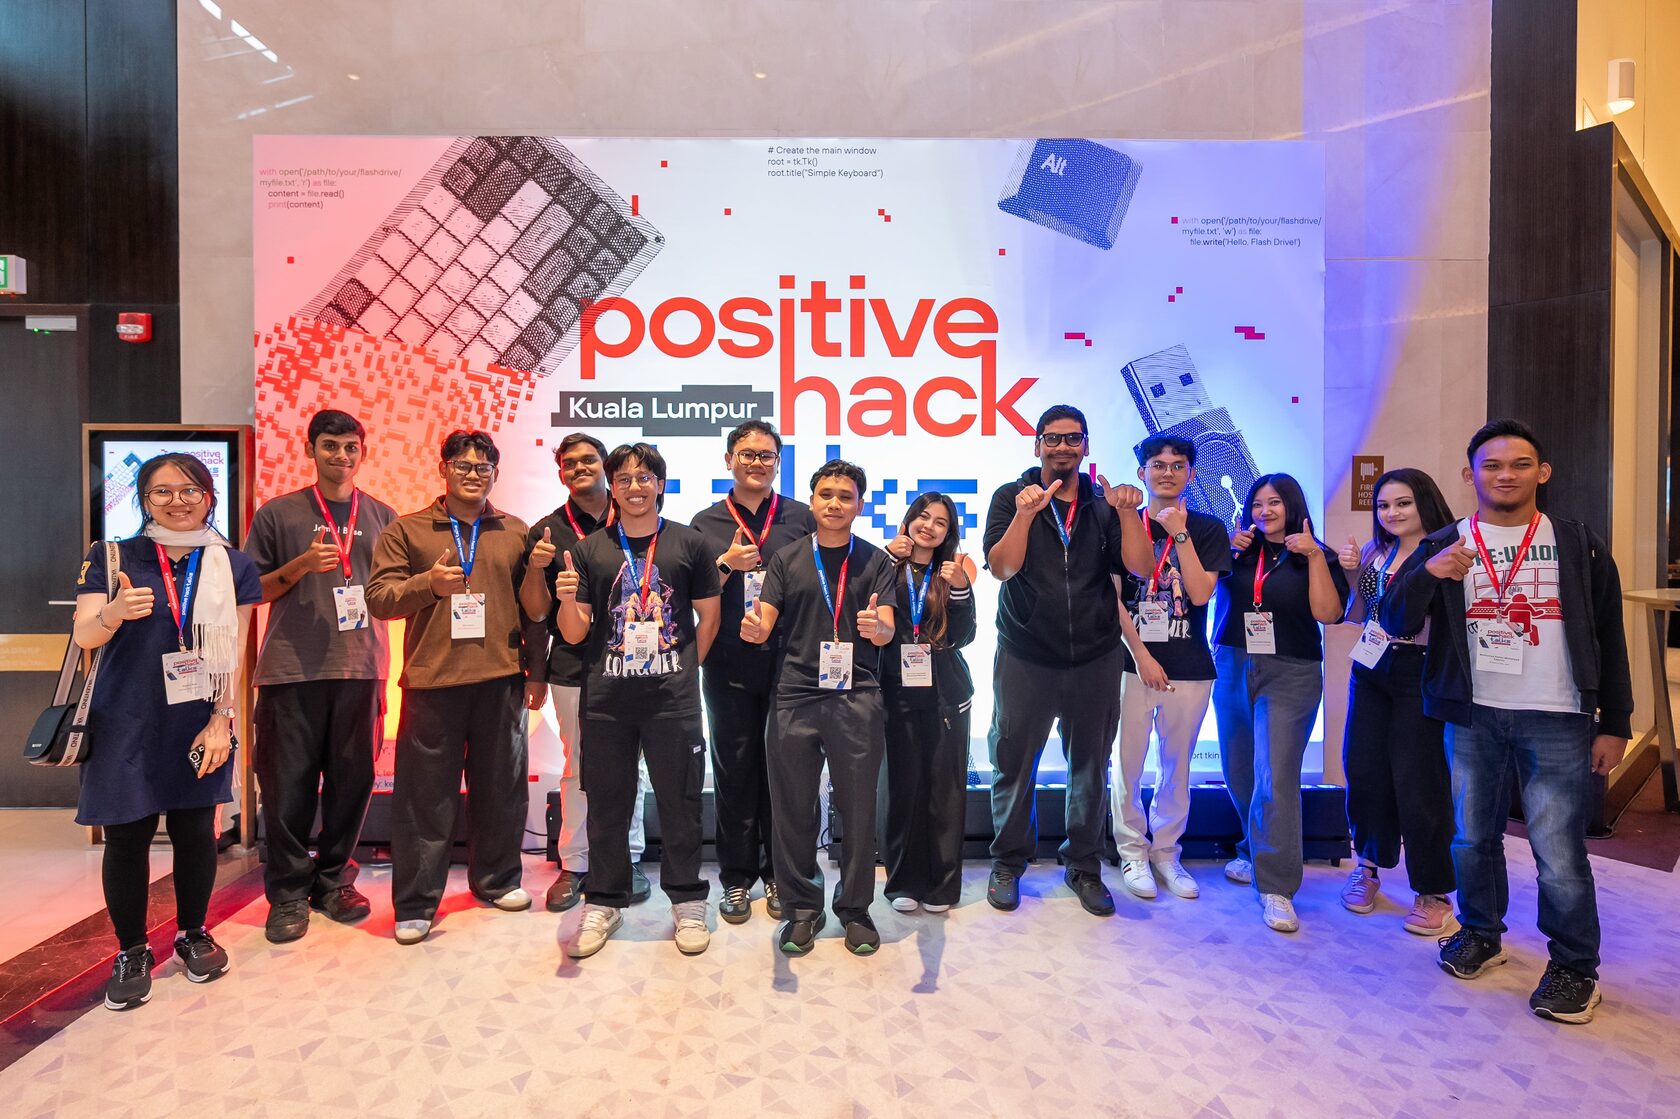
Thank you, KL! Real work on stage, hard questions from the room — that is what these stops are for. See you at the next one.
Welcome to Positive Hack Talks!
Alex Moshkov
Community Bro at Positive Technologies
Muhammad Firdaus Amran
Security Analyst (Offensive)
Ravshan Rikhsiev
Security Researcher at ONESEC
Aditya Singh
Senior Security Researcher at Siemens Healthineers
Akshay Jain
Senior Product Security Engineer
No one stays hungry. We provide a full lunch.
Sayaan Alam
Security Researcher & Bug Bounty Hunter
Alexander Popov
Linux Kernel Developer and Security Researcher at Positive Technologies
Navenesh Kumar
Founder, I/O TRIX
Nik Amir Hakim & Adlina Batrisya
Lead Agent MCC & Security Researcher
Rectifyq
Security Analyst
Sagar Tiwari, Shubham Kumar
Independent Cybersecurity and OSINT Researcher · Senior Information Security Analyst & OSINT Researcher
Haidar Kabibo
Application Security Specialist at Kaspersky
Positive Technologies is an industry leader in result-driven cybersecurity and a major global provider of information security solutions. Over 4,000 organizations worldwide use technologies and services developed by our company.
In addition to developing cybersecurity products and solutions, the company organizes events and activities for everyone passionate about cybersecurity: from enthusiasts to professionals.
 PT CommunityWe build things for the security community and bring everybody together. Knowledge, tools, events, competitions — open and free for everyone.
 Positive Hack DaysAn international cyberfestival for those who want to dive into the world of cybersecurity and have a great time.
 Positive Hack CampAnnual international event for cybersecurity beginners from around the globe to gain insights from leading specialists in IT infrastructure protection and cybersecurity.
 Cybersecurity calendarEvery conference, CFP and meetup — in one place.
 @ptswarmWhere the Positive Technologies Offensive Team shares their latest findings, exploits, and deep-technical write-ups.
 dbu.gsThe most complete and up-to-date vulnerability database with researcher profiles, AI summaries, and trending analysis.
 Standoff Bug BountyA bug bounty platform with generous rewards for discovering vulnerabilities in top companies.